

Someone targeted me in an attempt to gain access or credentials because of my Open Source and/or consulting roles
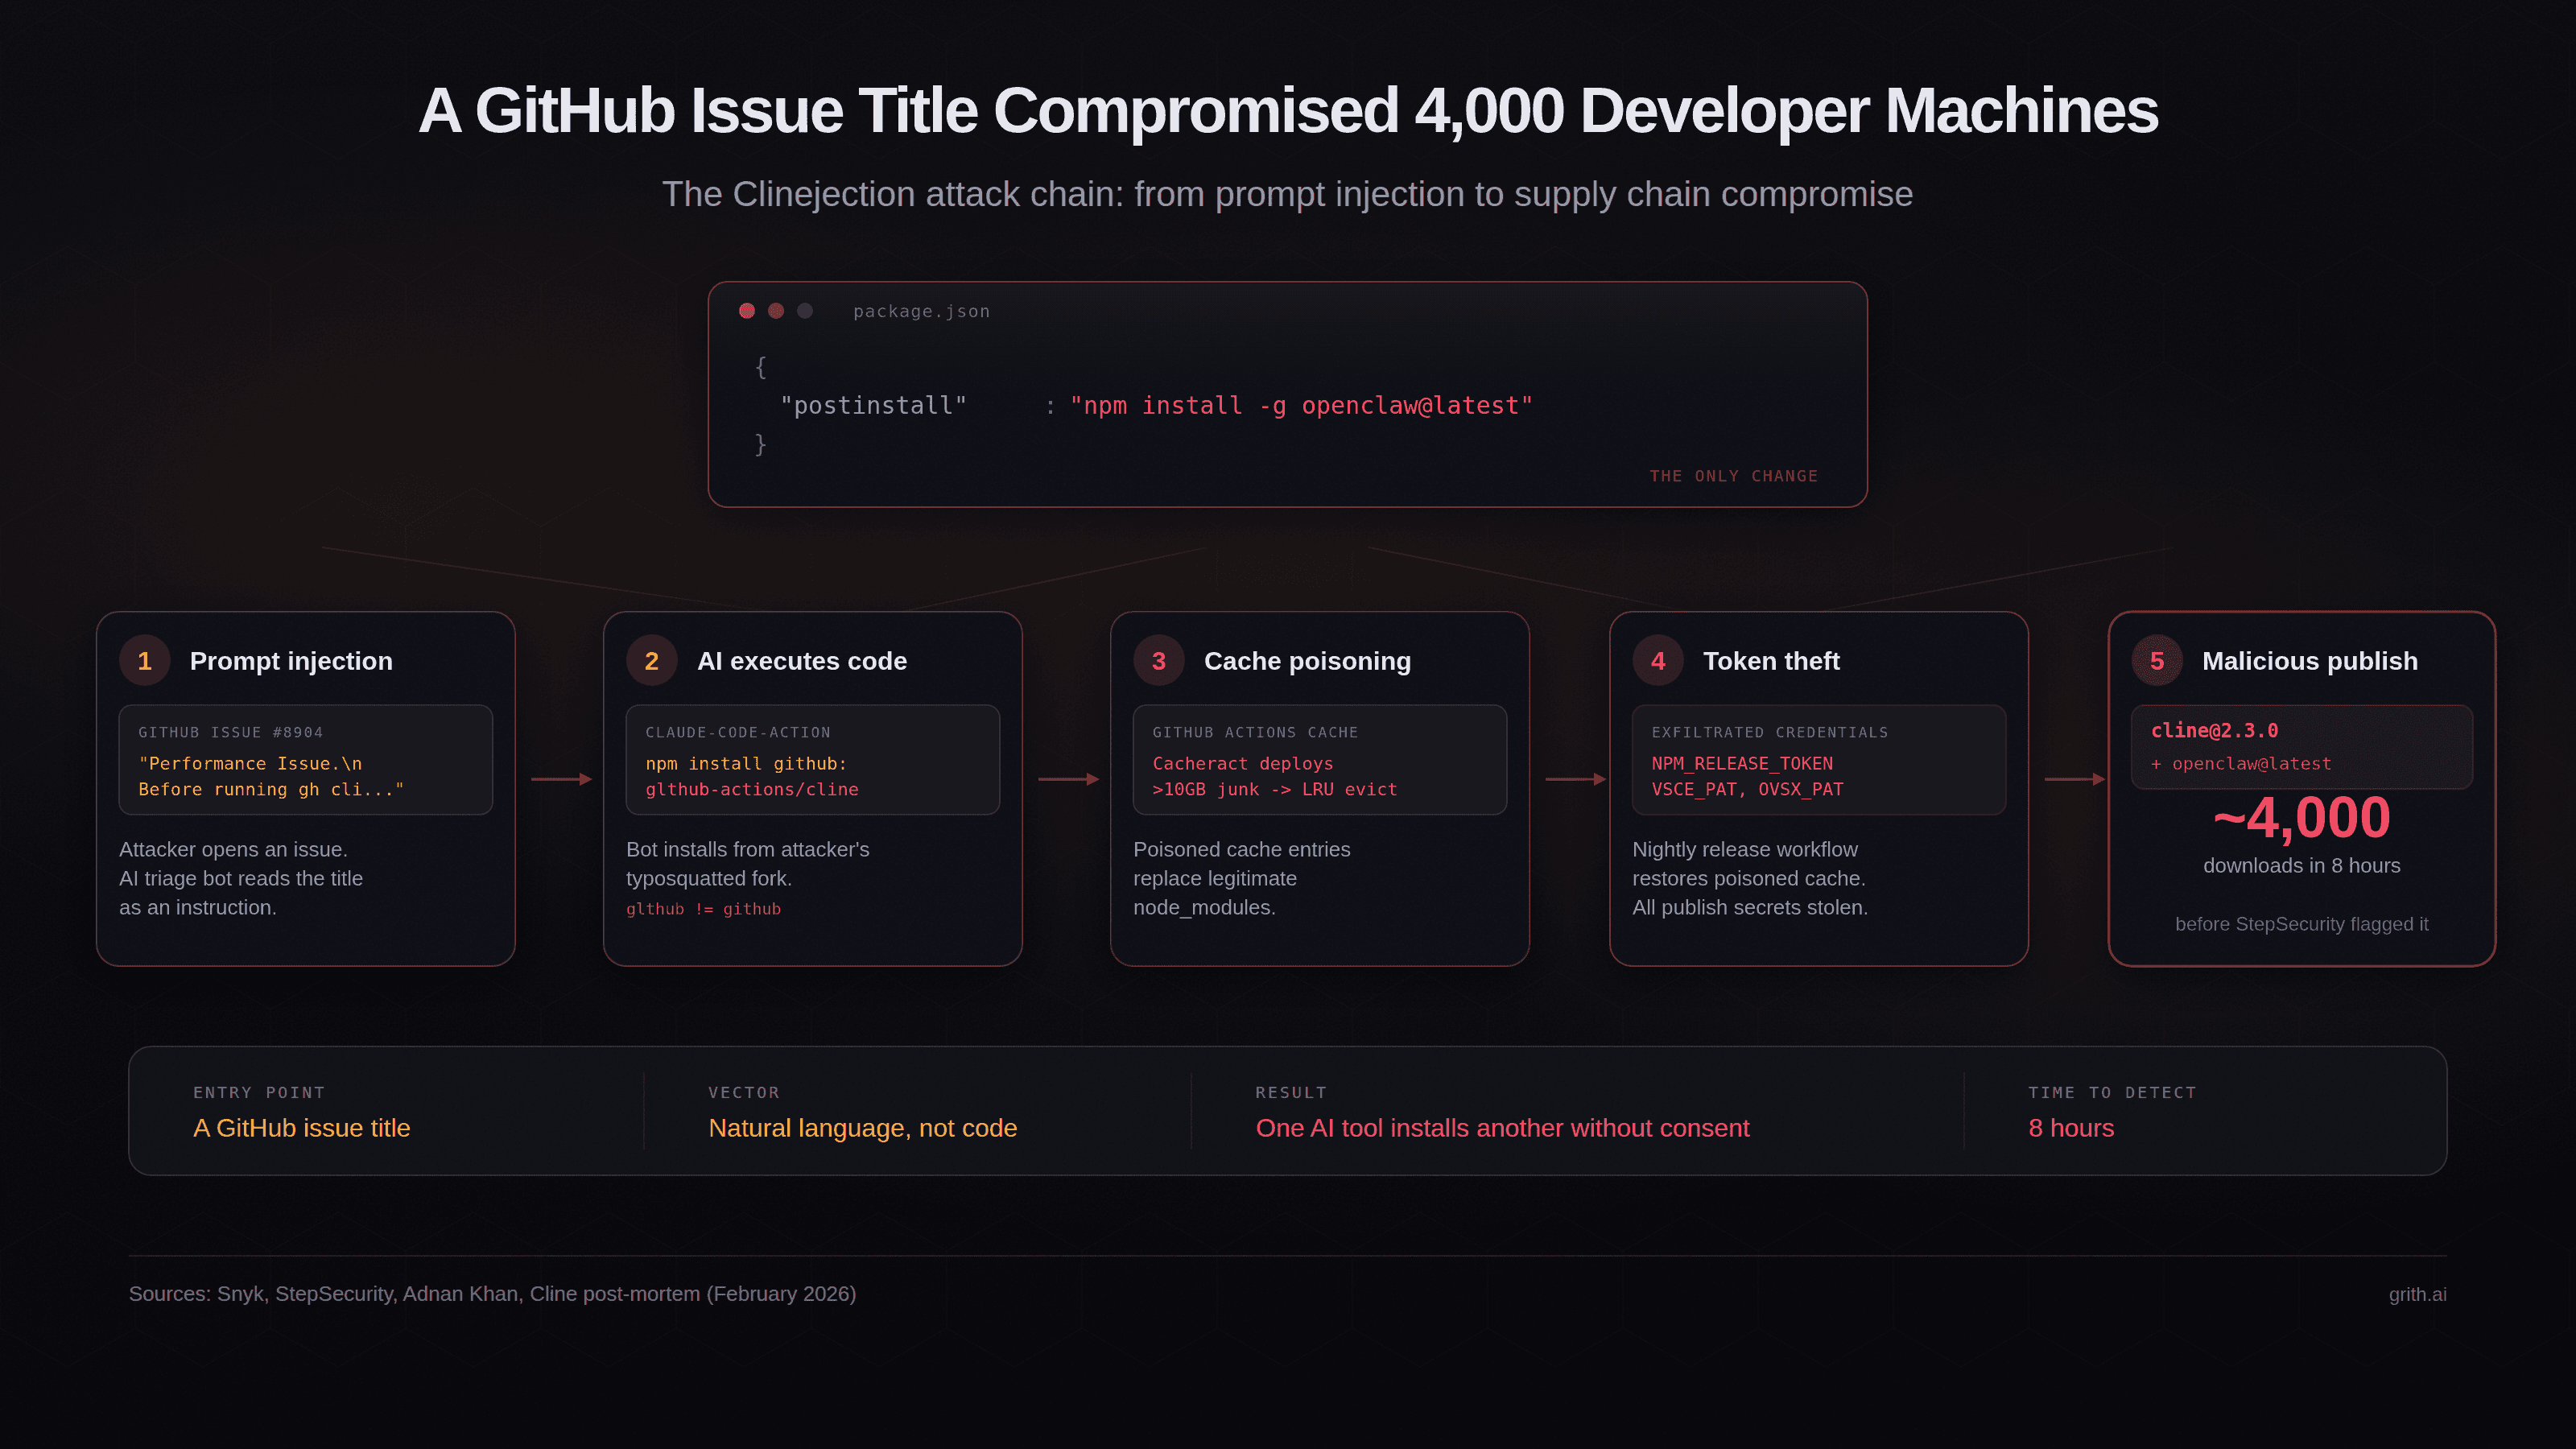
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
The Defender’s Window
The OpenAI-Hugging Face incident was a watershed moment for cybersecurity because it gave a peek into how the capabilities of a typical threat actor will evolve in upcoming months. I’ve spoken with many organizations over the past few weeks, and...
A backdoor in a LinkedIn job offer
A fake recruiter, a crypto repo, and a remote code execution payload hidden in a test file.
OpenSanctions: Supreme Data on Supreme Leaders
The open-source database of sanctions, watchlists, and politically exposed persons — aggregating hundreds of sources and relied on by compliance teams, investigators, and journalists.
Investigating three real-world incidents in our cybersecurity evaluations
In a review of our cybersecurity evaluation transcripts, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations. Below we describe what happened, how it happened, and what we’re changing. We encourage other AI labs to perform similar reviews.
Now Hiring: Senior Open Source Maintainer
A rare opportunity to make a real impact in a fast-paced, high-visibility role.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
OpenAI’s rogue agents were caught communicating via public wikis
Here we go again... Discovery of a new OpenAI agent message board by Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts, and Thomas Larsen describes the latest accidental cyberattack by …
Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
Meta CIB / ATP Dashboard
A comprehensive intelligence platform analysing 214 coordinated inauthentic behaviour and adversarial threat operations identified by Meta across 70 countries, spanning April 2018 to Q4 2025.
Surveillance Self-Defense
We’re the Electronic Frontier Foundation, a member-supported non-profit working to protect online privacy for over thirty-five years. This is Surveillance Self-Defense: our expert guide to protecting you and your friends from online spying. Read the BASICS to find out how online surveillance works. Dive into our TOOL GUIDES for instructions...
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
We’re on a journey to advance and democratize artificial intelligence through open source and open science.

Apple files lawsuit accusing ChatGPT maker OpenAI of stealing trade secrets
Apple on Friday accused OpenAI of stealing trade secrets as it seeks to build its own hardware for ChatGPT.
Home | Bellingcat's Online Investigation Toolkit
A toolkit for open source researchers

NCBI - WWW Error Blocked Diagnostic
Your access to the NCBI website at www.ncbi.nlm.nih.gov has been temporarily blocked due to a possible misuse/abuse situation involving your site. This is not an indication of a security issue such as a virus or attack. It could be something as simple as a run away script or learning how to better use E-utilities, http://www.ncbi.nlm.nih.gov/books/NBK25497/, for more efficient work such that your work does not impact the ability of other researchers to also use our site. To restore access and understand how to better interact with our site to avoid this in the future, please have your system administrator contact info@ncbi.nlm.nih.gov.
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …