Our article 'Fighting the AI scraper bot scourge', published in early 2025, discussed the probl [...]
Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
Unlawful by design: Exposing the human rights costs of generative AI - Amnesty International
This briefing examines how standalone generative AI systems, based on unlawful web scraping, are in conflict with international human rights law (IHRL) and standards through their design, development and deployment. While these technologies promise sophisticated automation and efficiency, they rely on data collection and model training practices that abuse privacy rights, enable discrimination, and threaten […]
Solving Fossil SCM's CAPTCHA in 171 characters | nns.ee
Ethical Hacking and Cybersecurity Blog
AI Agent Executes 'First' End-To-End Ransomware Attack - Slashdot
Sysdig says it has documented the first ransomware attack carried out end to end by an AI agent, which autonomously exploited exposed systems, stole credentials, established persistence, compromised a production database, and destroyed data. The research team named the attacker "JadePuffer" and said...

Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
Track, control, and optimize for AI agents and bots | Known Agents (formerly Dark Visitors)
Use Known Agents to turn the rising wave of AI agents, LLM assistants, and other bots crawling your website into a new growth channel for your business
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
A quote from Daniel Stenberg
The challenge with AI in open source security has transitioned from an AI slop tsunami into more of a ... plain security report tsunami. Less slop but lots of reports. …
We mourn our craft
I didn’t ask for this and neither did you. I didn’t ask for a robot to consume every blog post and piece of code I ever wrote and parrot it back so that some hack could make money off o…

Investigating three real-world incidents in our cybersecurity evaluations
In a review of our cybersecurity evaluation transcripts, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations. Below we describe what happened, how it happened, and what we’re changing. We encourage other AI labs to perform similar reviews.
AI Wrappers: It's Just Trucks All The Way Down
Check out this programming meme on ProgrammerHumor.io
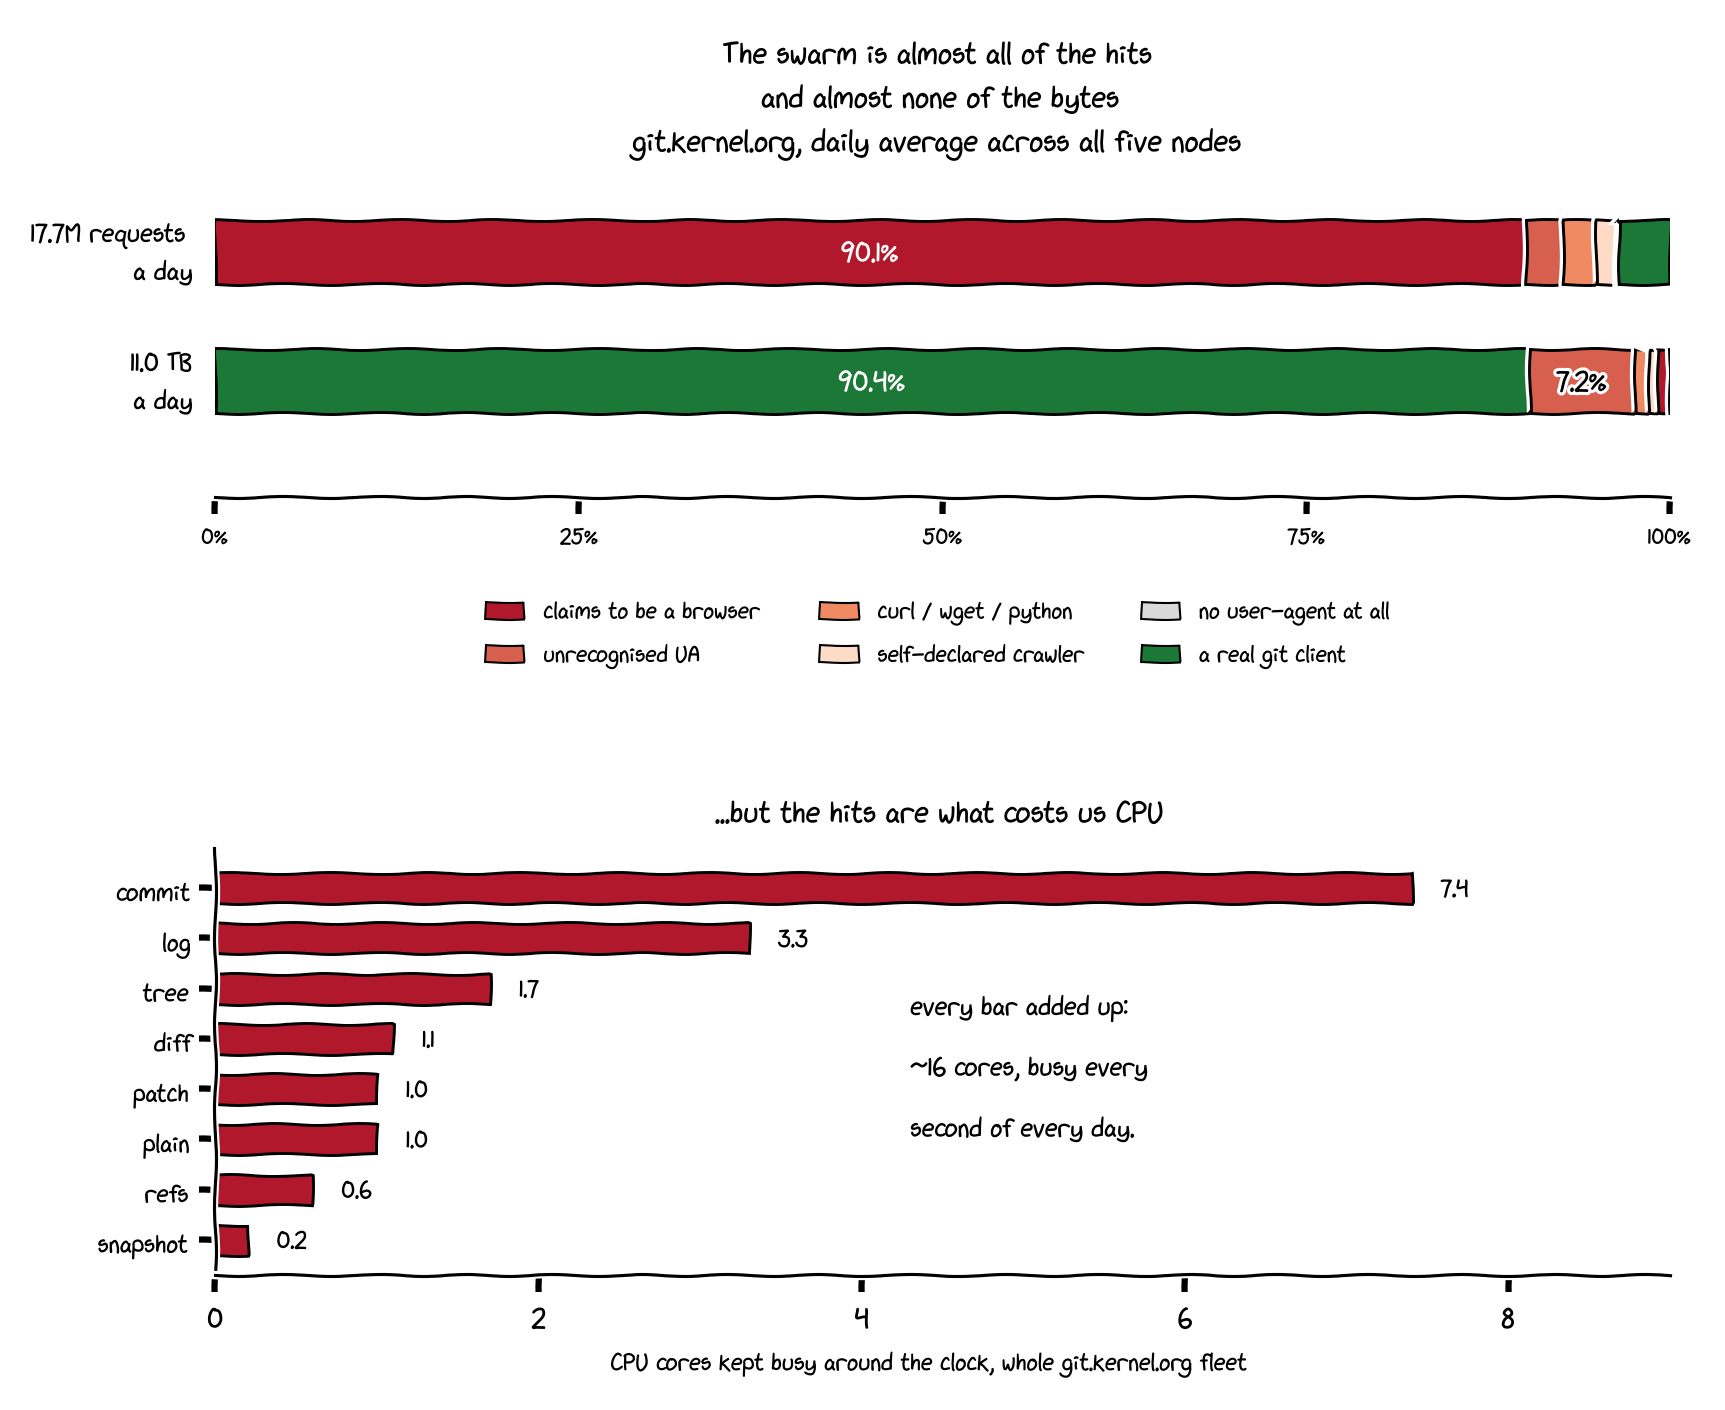
Creepy crawlies — Konstantin Ryabitsev
You've probably heard me complain about the "AI crawlers" before, but now I actually have some hard numbers I can put up to show their im...
Cybersecurity Looks Like Proof of Work Now
The UK's AI Safety Institute recently published Our evaluation of Claude Mythos Preview’s cyber capabilities, their own independent analysis of Claude Mythos which backs up Anthropic's claims that it is …
AI Cybersecurity After Mythos: The Jagged Frontier
When AISLE tested Mythos's showcase vulnerabilities on small, cheap, open-weights models, most found the same bugs. Here's what that means for cyber.
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
We’re on a journey to advance and democratize artificial intelligence through open source and open science.

More Than a Tool
What We Learned from a Year of Conversations About AI