


Claude Mythos Preview is a new general-purpose language model that is strikingly capable at computer security tasks. This post provides technical details for researchers and practitioners who want to understand exactly how we have been testing this model, and what we have found over the past month.
Cybersecurity Looks Like Proof of Work Now
The UK's AI Safety Institute recently published Our evaluation of Claude Mythos Preview’s cyber capabilities, their own independent analysis of Claude Mythos which backs up Anthropic's claims that it is …
AI Cybersecurity After Mythos: The Jagged Frontier
When AISLE tested Mythos's showcase vulnerabilities on small, cheap, open-weights models, most found the same bugs. Here's what that means for cyber.
Investigating three real-world incidents in our cybersecurity evaluations
In a review of our cybersecurity evaluation transcripts, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations. Below we describe what happened, how it happened, and what we’re changing. We encourage other AI labs to perform similar reviews.
Project Glasswing: Securing critical software for the AI era
A new initiative to secure the world’s most critical software and give defenders a durable advantage in the coming AI-driven era of cybersecurity.
A quote from Daniel Stenberg
The challenge with AI in open source security has transitioned from an AI slop tsunami into more of a ... plain security report tsunami. Less slop but lots of reports. …
The Defender’s Window
The OpenAI-Hugging Face incident was a watershed moment for cybersecurity because it gave a peek into how the capabilities of a typical threat actor will evolve in upcoming months. I’ve spoken with many organizations over the past few weeks, and...
Guardian Angels: LLM Personalization for Productivity and Security
I propose an approach for highly personalized LLMs, for near-future productivity gains and personal info/cybersecurity against increasingly powerful LLMs: they should, in the spirit of uploading, try to emulate the user’s values and preferences in order to amplify the principal—not replace them. I discuss a package of techniques and proposals to accomplish such ‘guardian angels’; dynamic evaluation of LLMs combined with active learning and elicitation and heavy inner-monologue search/data-augmentation.
Surveillance Self-Defense
We’re the Electronic Frontier Foundation, a member-supported non-profit working to protect online privacy for over thirty-five years. This is Surveillance Self-Defense: our expert guide to protecting you and your friends from online spying. Read the BASICS to find out how online surveillance works. Dive into our TOOL GUIDES for instructions...
Pony
An open-source, object-oriented, actor-model, capabilities-secure, high-performance programming language.
OpenAI and Hugging Face partner to address security incident during model evaluation
OpenAI and Hugging Face share early findings from a security incident during AI model evaluation, highlighting advanced cyber capabilities and lessons for defenders.

Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
Introducing the 2026 Cloudflare Threat Report
There has been a fundamental shift toward industrialized cyber threats, highlighted by a record 31.4 Tbps DDoS attack and sophisticated session token theft. Our new report examines how nation-states and criminal actors have moved beyond traditional exploits to "living off the XaaS" within legitimate enterprise logic.

Solving Fossil SCM's CAPTCHA in 171 characters | nns.ee
Ethical Hacking and Cybersecurity Blog
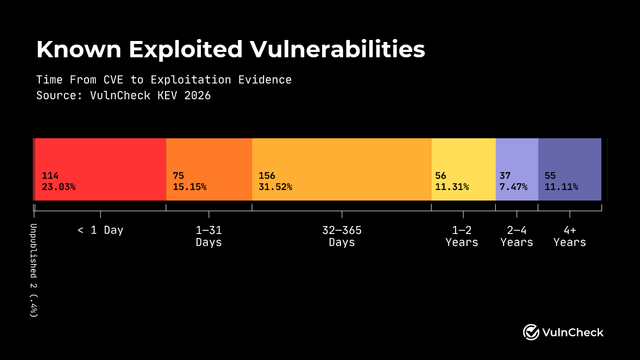
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
COMPOST Special Issue: Stop Surveillance Copaganda
Anti-surveillance stories, reactions, analysis, and incitement built by privacy activists and human rights experts, in collaboration with Strange Horizons as well as the DWeb Camp, DragonCon, and RightsCon communities. The toolkit is now available globally and for free to all creators who want to write more dynamic stories that challenge fascist repression via surveillance tech.